Our data security AI copilot

Less time documenting risk. More time eliminating it.

Most data security tools stop at the finding.

Sensitive data spreads across environments, into external hands, and into AI tools and workflows. Finding it is the part the industry has been focused on solving.

What comes after is still manual. Someone has to work out which findings actually matter, decide the right action for each one, and carry that action out consistently across every resource, often without knowing where to start. That work is slow, it varies by whoever is doing it, and it is hard to prove after the fact.

Reporting is its own tax. The CISO update, the legal readout, and the audit evidence all get assembled by hand from the same numbers, then rebuilt whenever the audience changes.

Kosmo closes that gap.

The urgency is real. Automation isn't.

Security leaders name AI data exposure and data sprawl as the two biggest risks for next year, ahead of identity, cloud, compliance, and third-party risk combined. Half still call remediation mostly or fully manual, even with a mature stack already in place.

The math doesn't work

The average team reviews 195 alerts a day. A conservative 5% high-priority share is still about 10 alerts, enough to eat a full day for a lean 3-person team before the routine queue even opens.

Speed is an illusion

63% resolve their top incident in under 4 hours. What created the exposure, a pasted prompt, a file copied to a new SaaS tool, was instant. Hours is a luxury security teams don't have in an AI-first world.

The backlog is real

43% still carry unresolved high-priority alerts a week later.

Existing tools are binary.

Alert or don't, block or allow. They weren't built to choose among non-binary remediation actions for a specific piece of data, in real time.
Teleskope customers reach up to 87% automation on data security alerts.

See Kosmo in action.

Five steps, one agent.

Kosmo

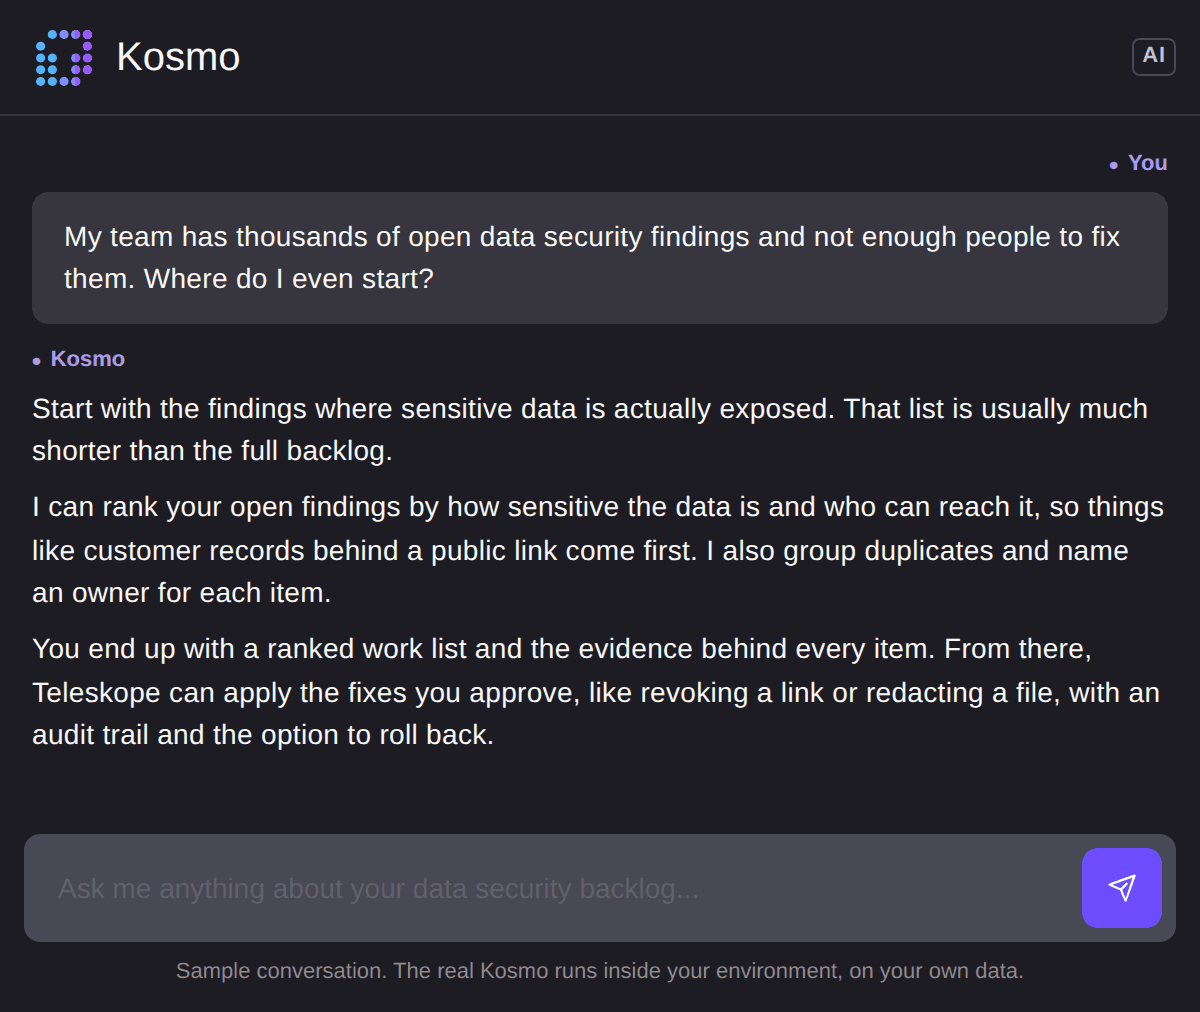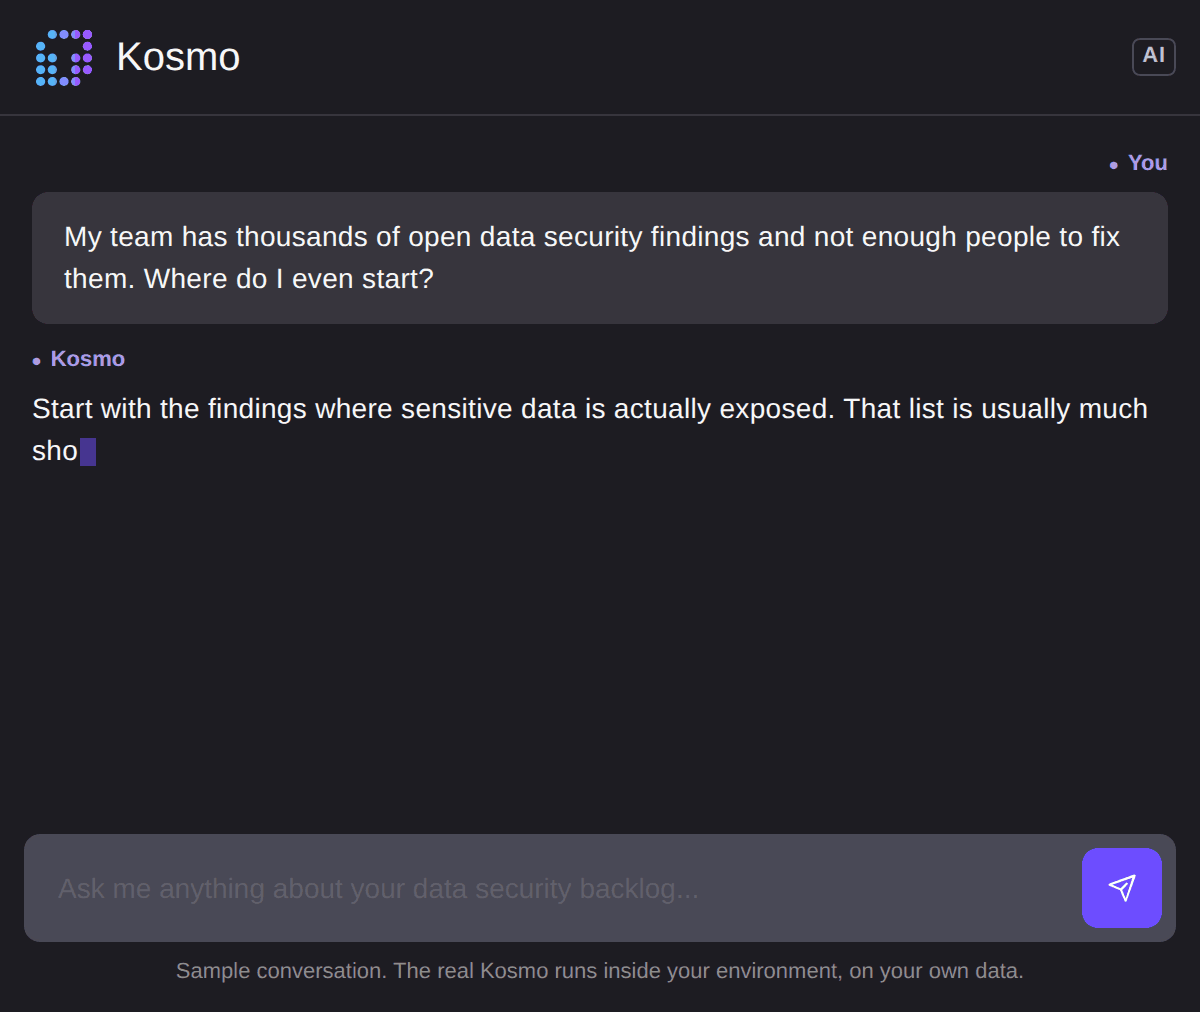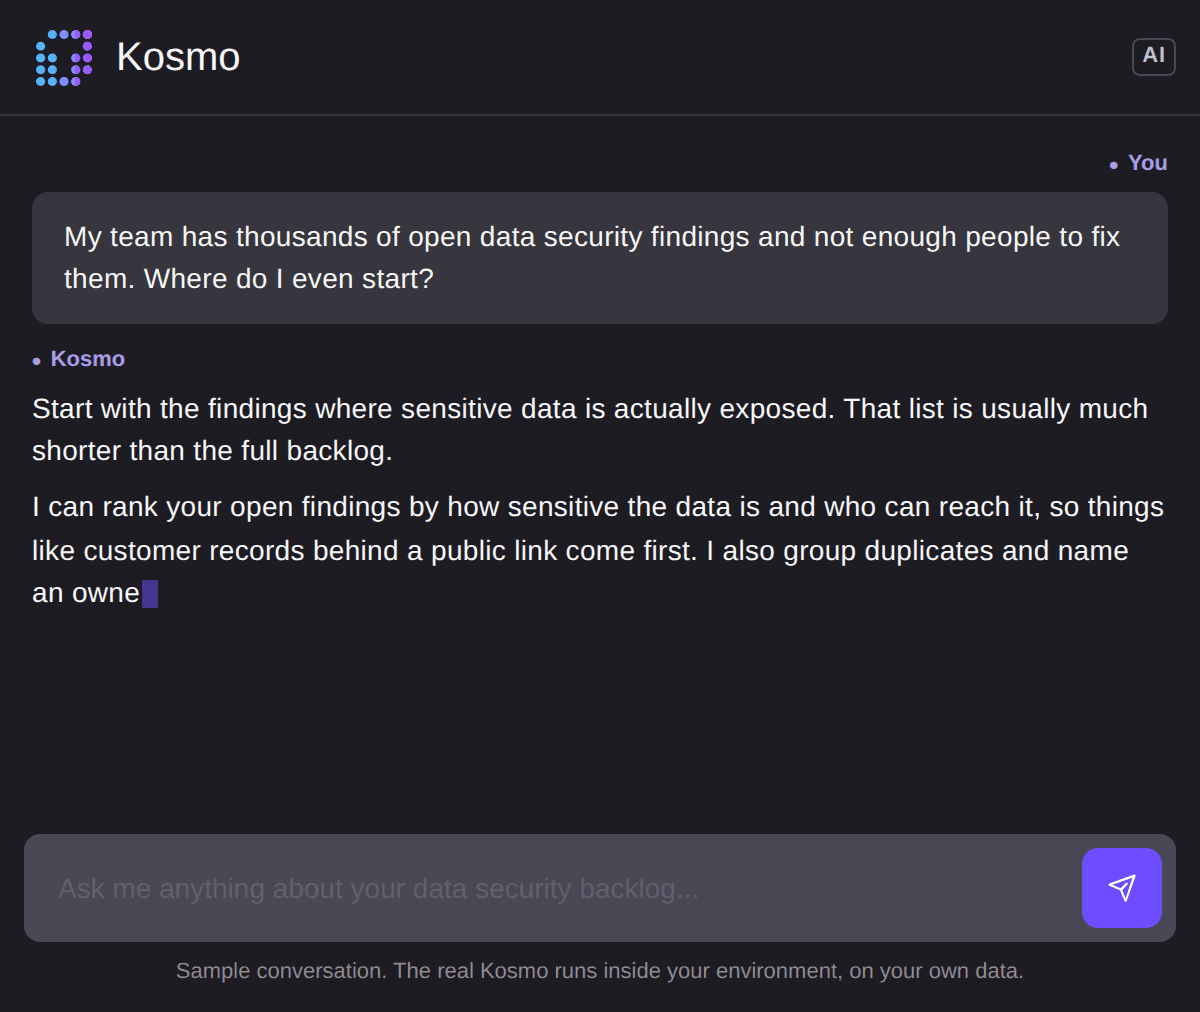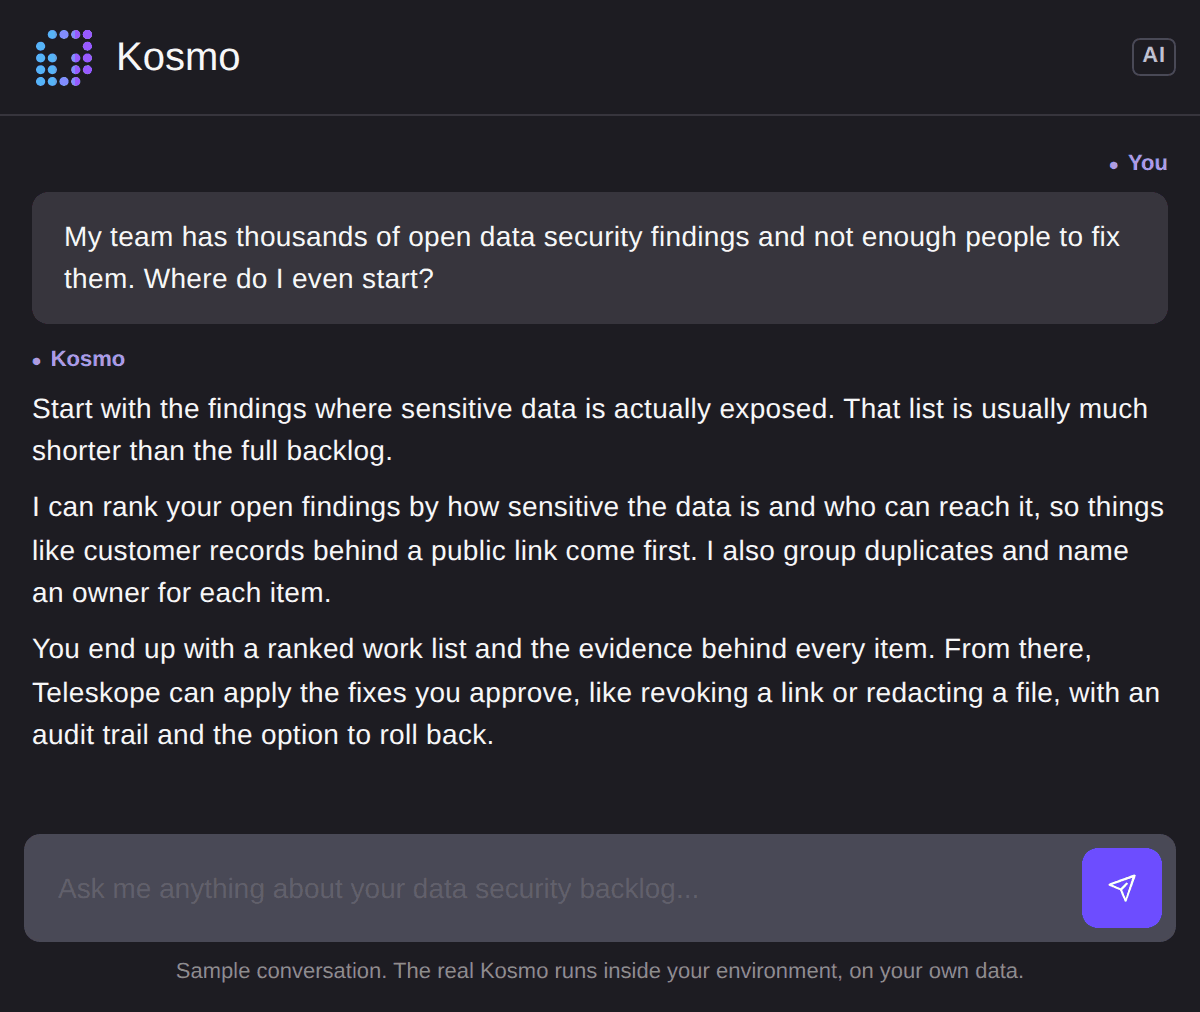
Ask in plain language

Ask Kosmo about a specific location, such as the risk inside a product testing folder. It searches that path and returns a summary of what it found: the sensitivity risk, where criticality differs across files, which elements surfaced, and the source system the folder lives in.

‍

If the results are broad, Kosmo suggests how to narrow them. You do not need to know the platform first. Kosmo knows the discipline and it knows your estate, so it brings the method.
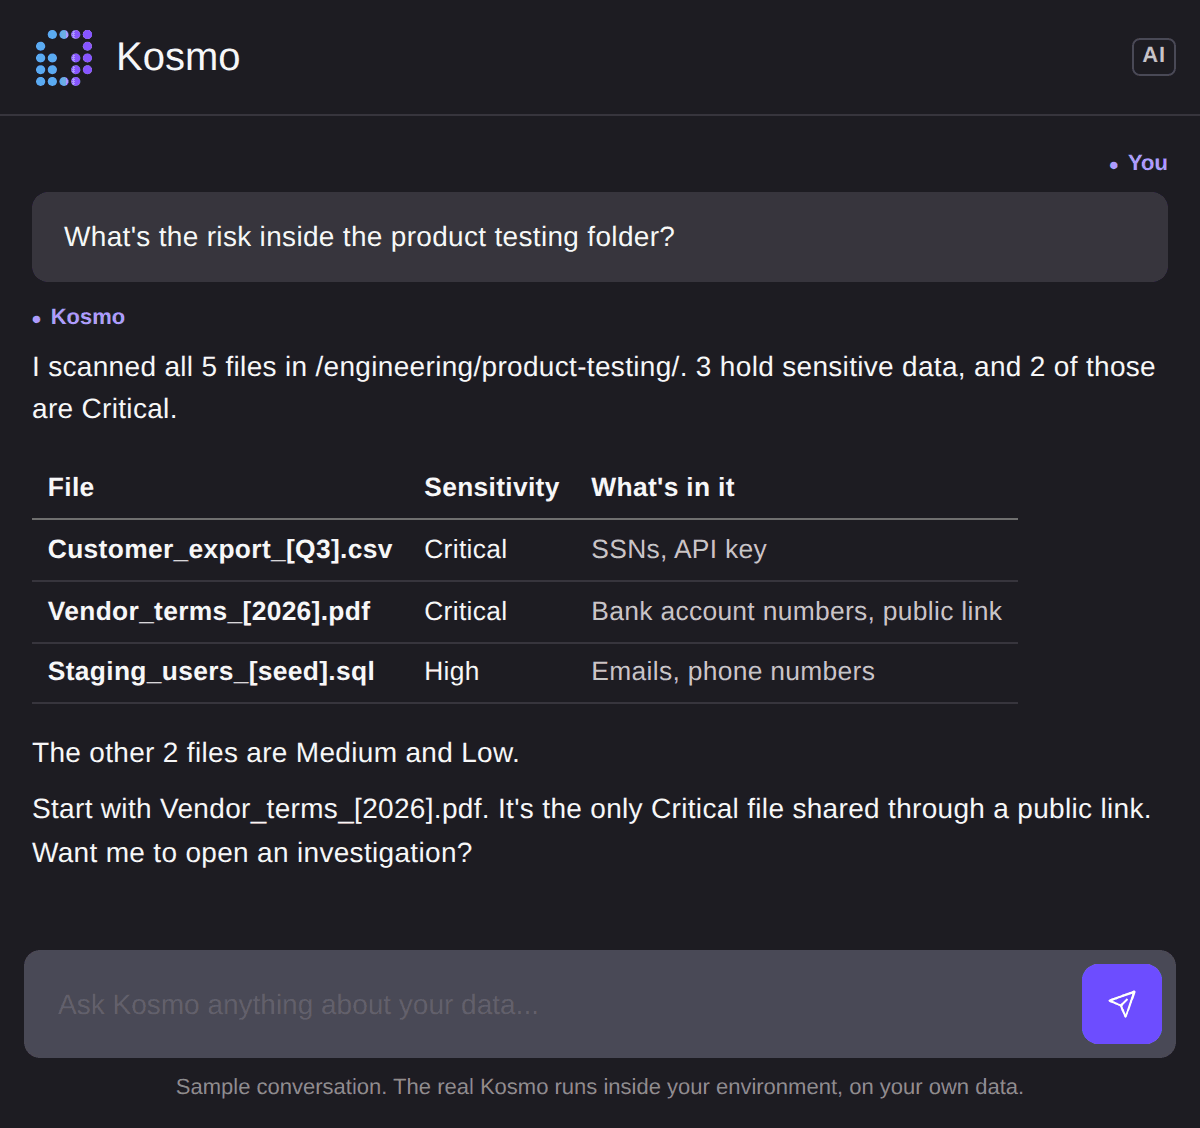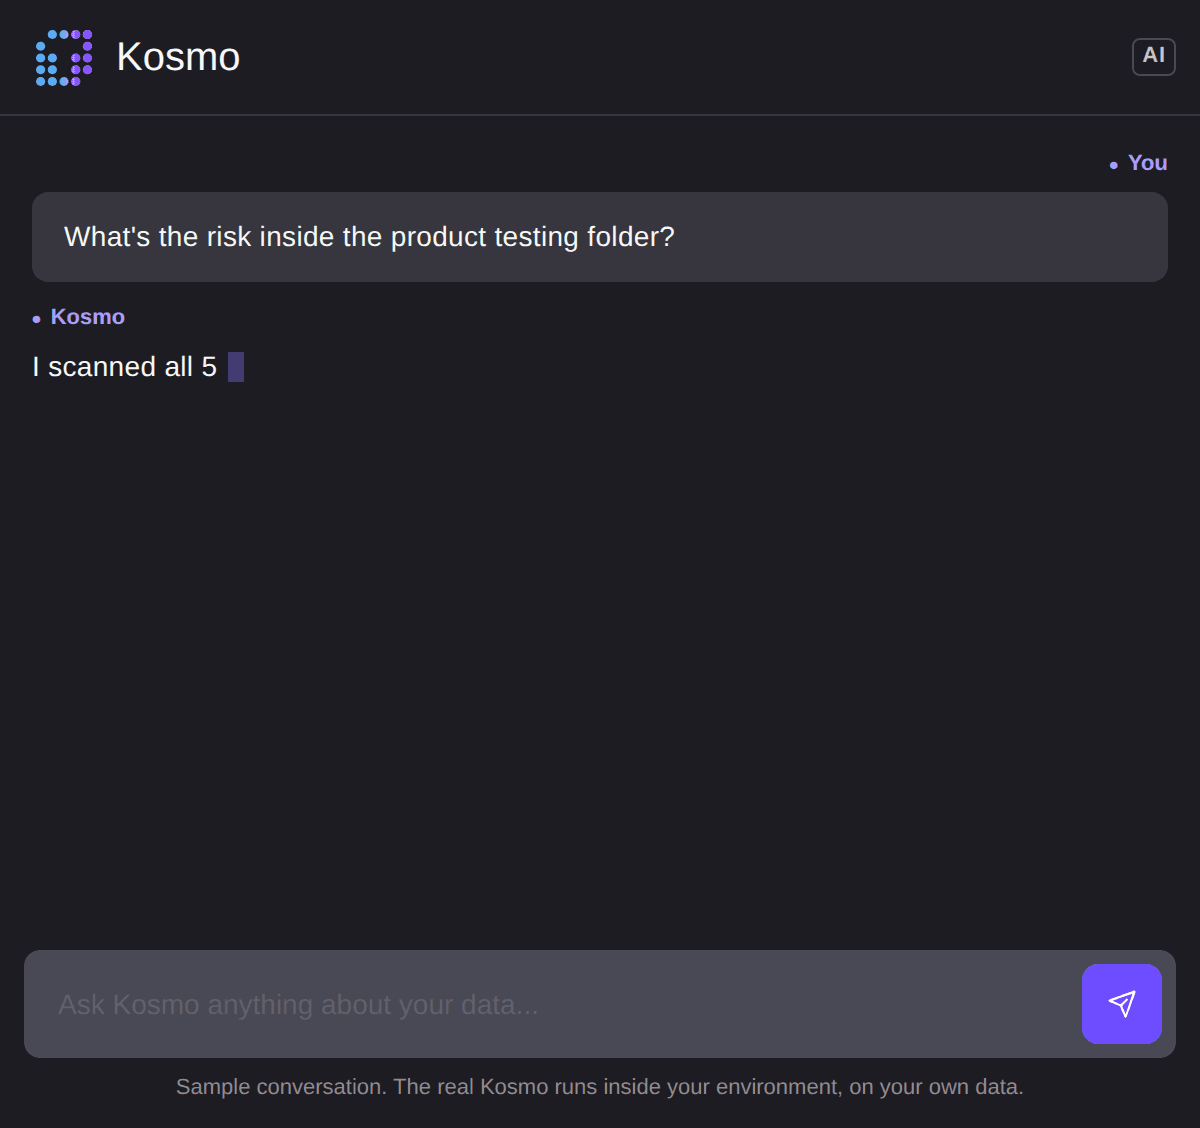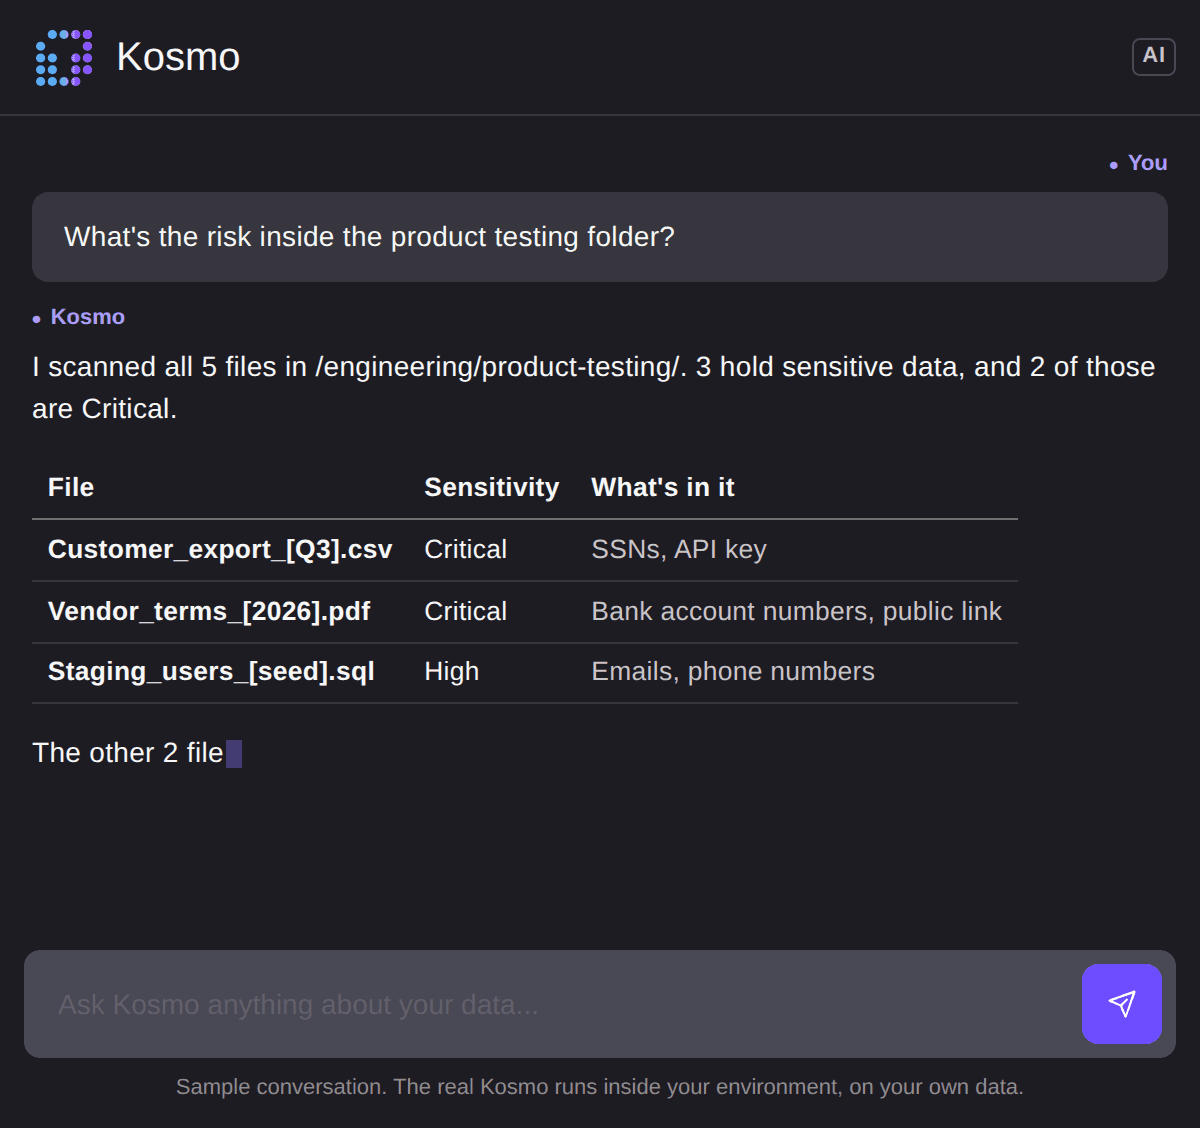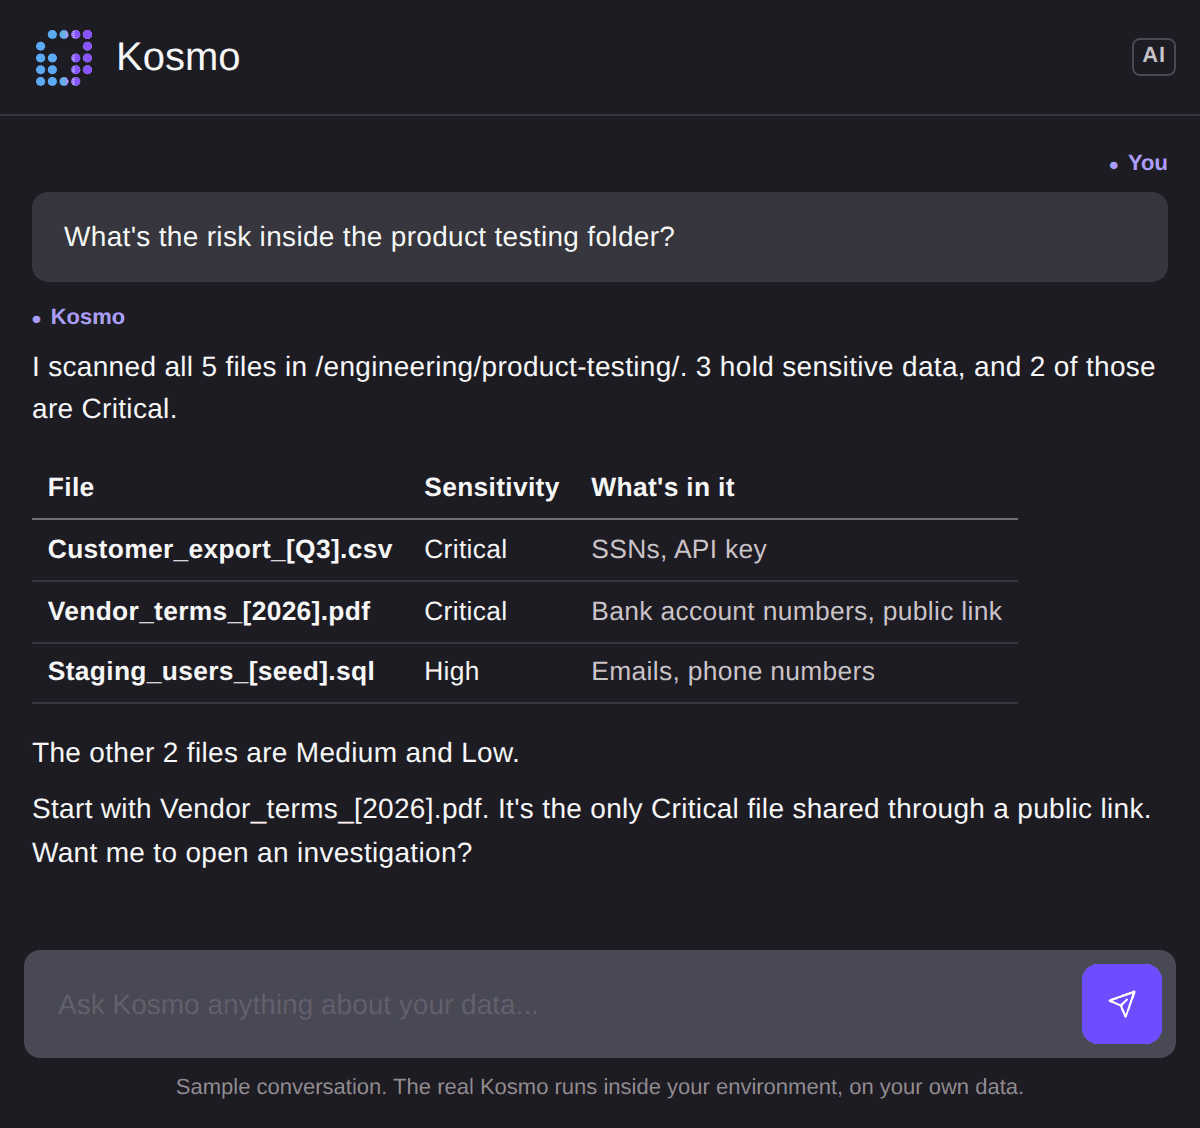
Kosmo — Plain language
Kosmo

Get a remediation plan

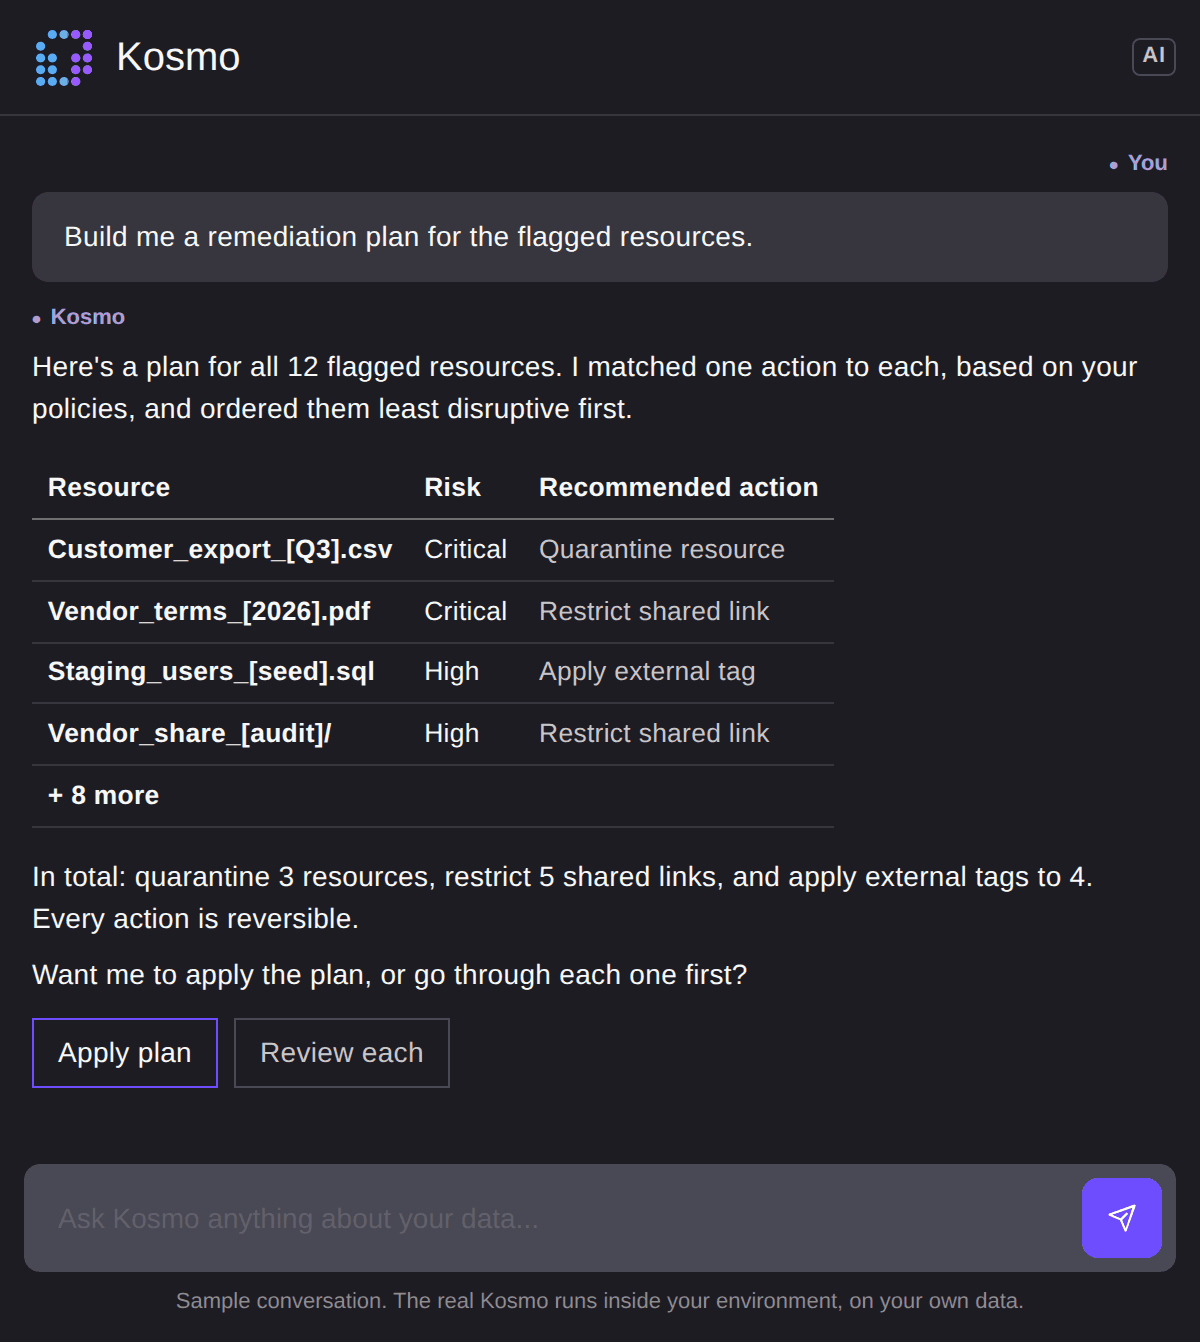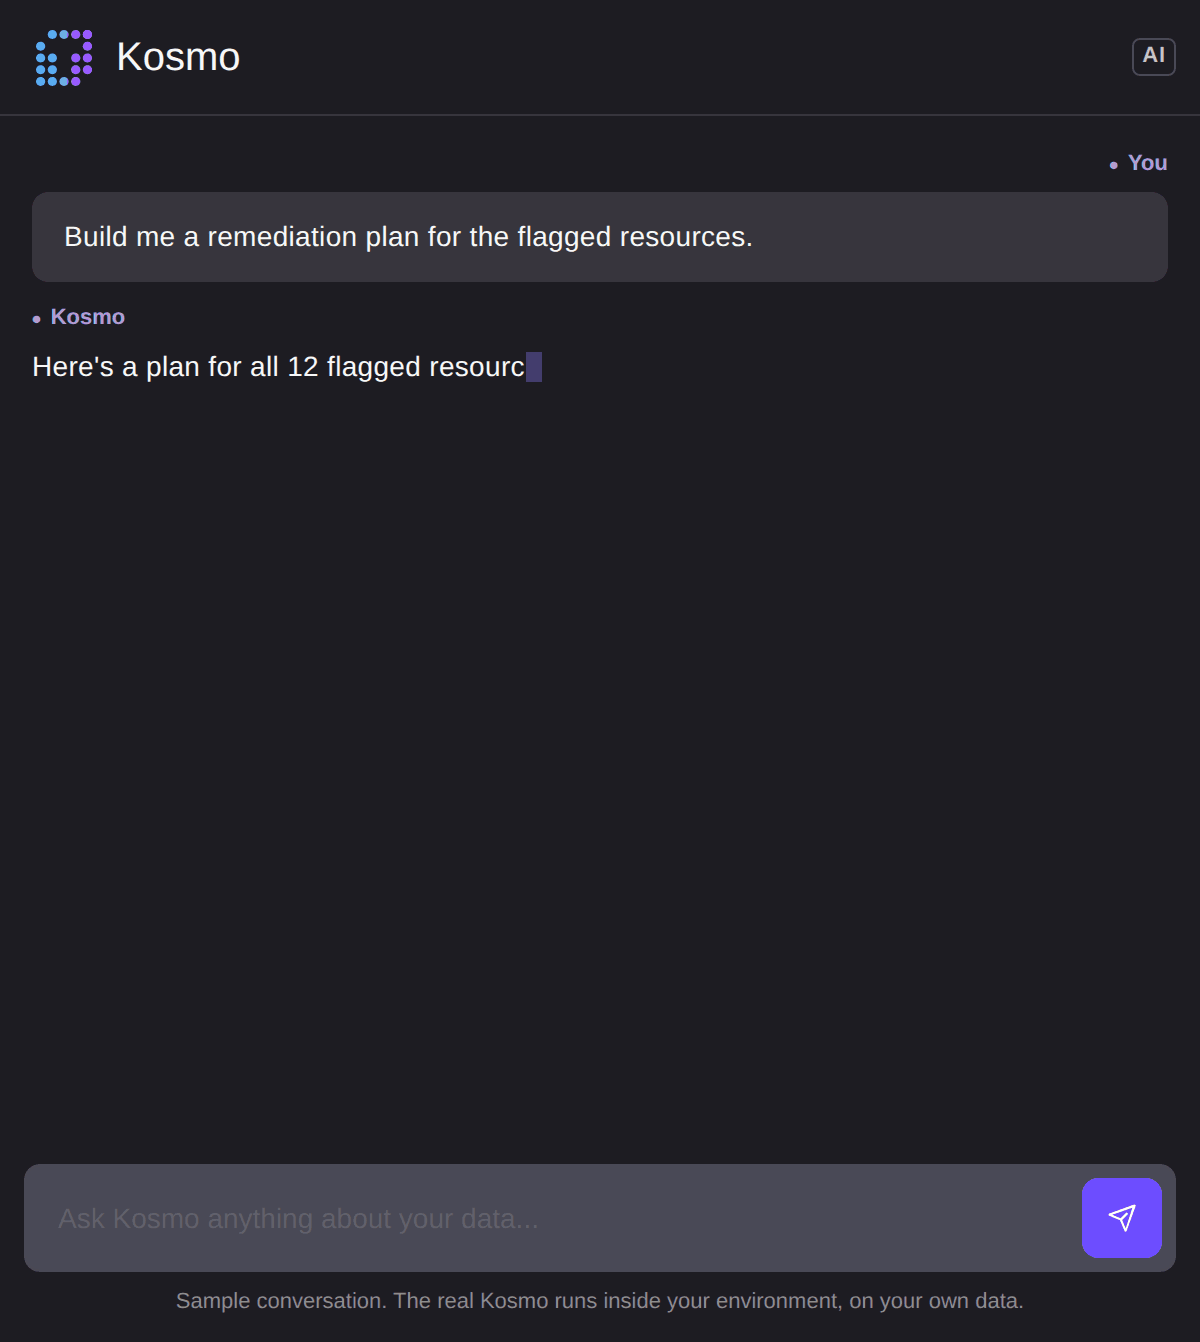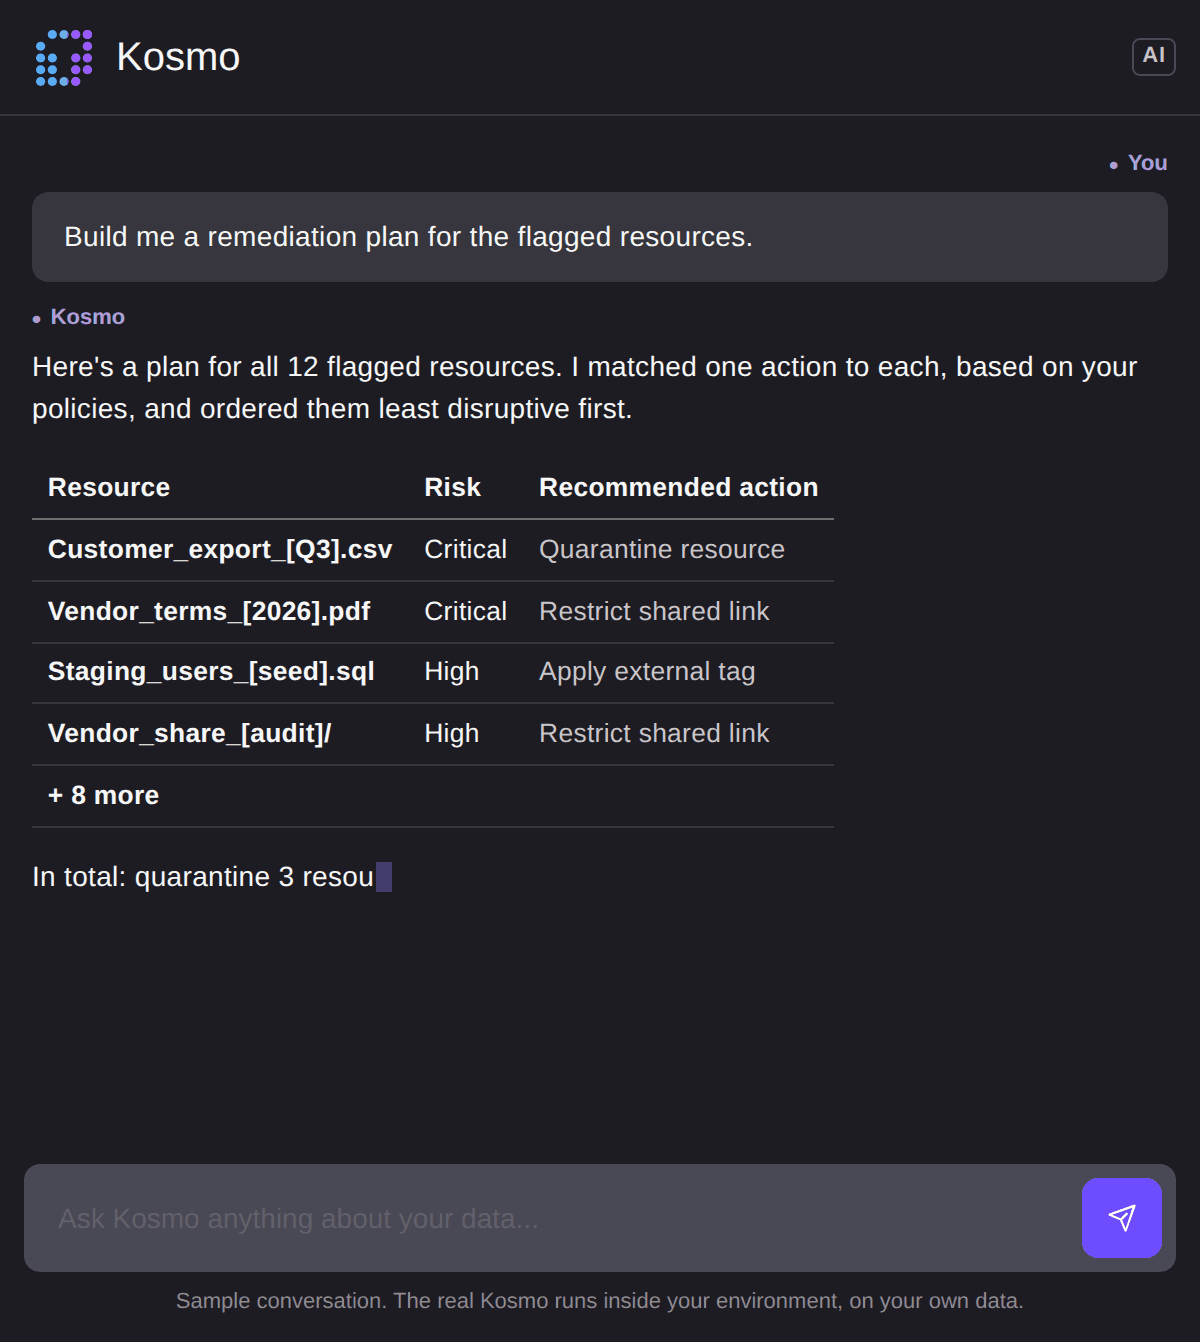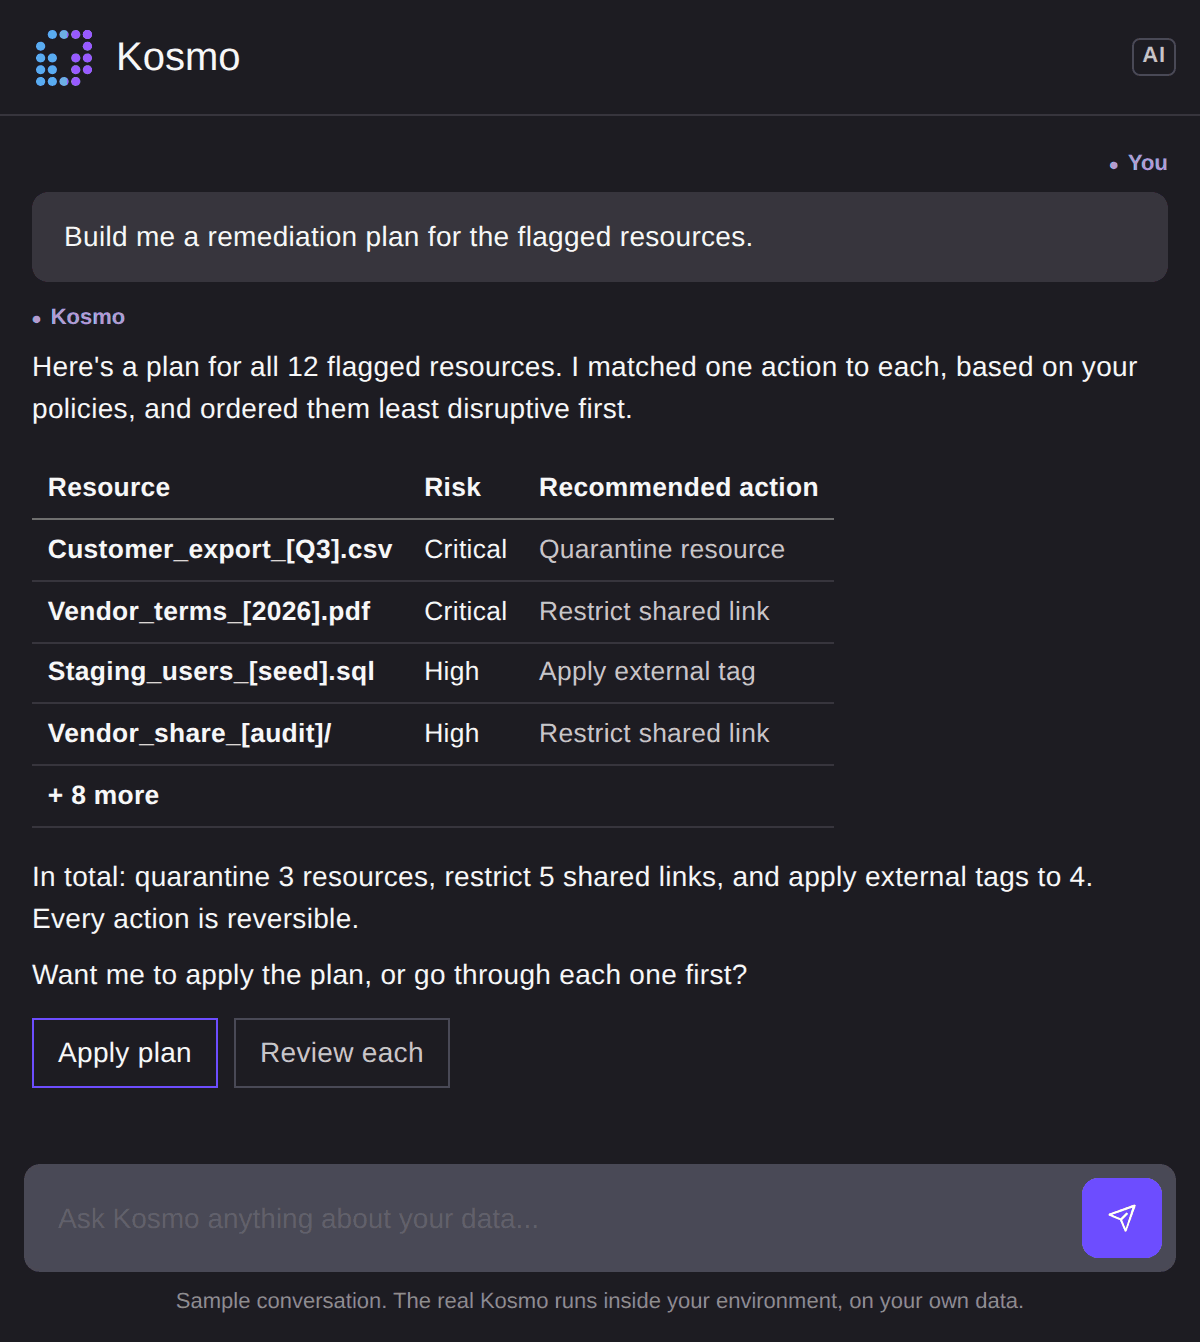
Ask for help remediating and Kosmo builds a plan based on what it found, with a specific action matched to each file:

‍

  • Quarantine the resource
  • Restrict the shared link
  • Apply external tags

‍

The plan reflects your data, your policies, and your preferences. Kosmo starts with the least disruptive option, like alerting the data owner, and prefers reversible actions. You decide how far to go.

Kosmo — Remediation plan
Kosmo

Review, apply, verify

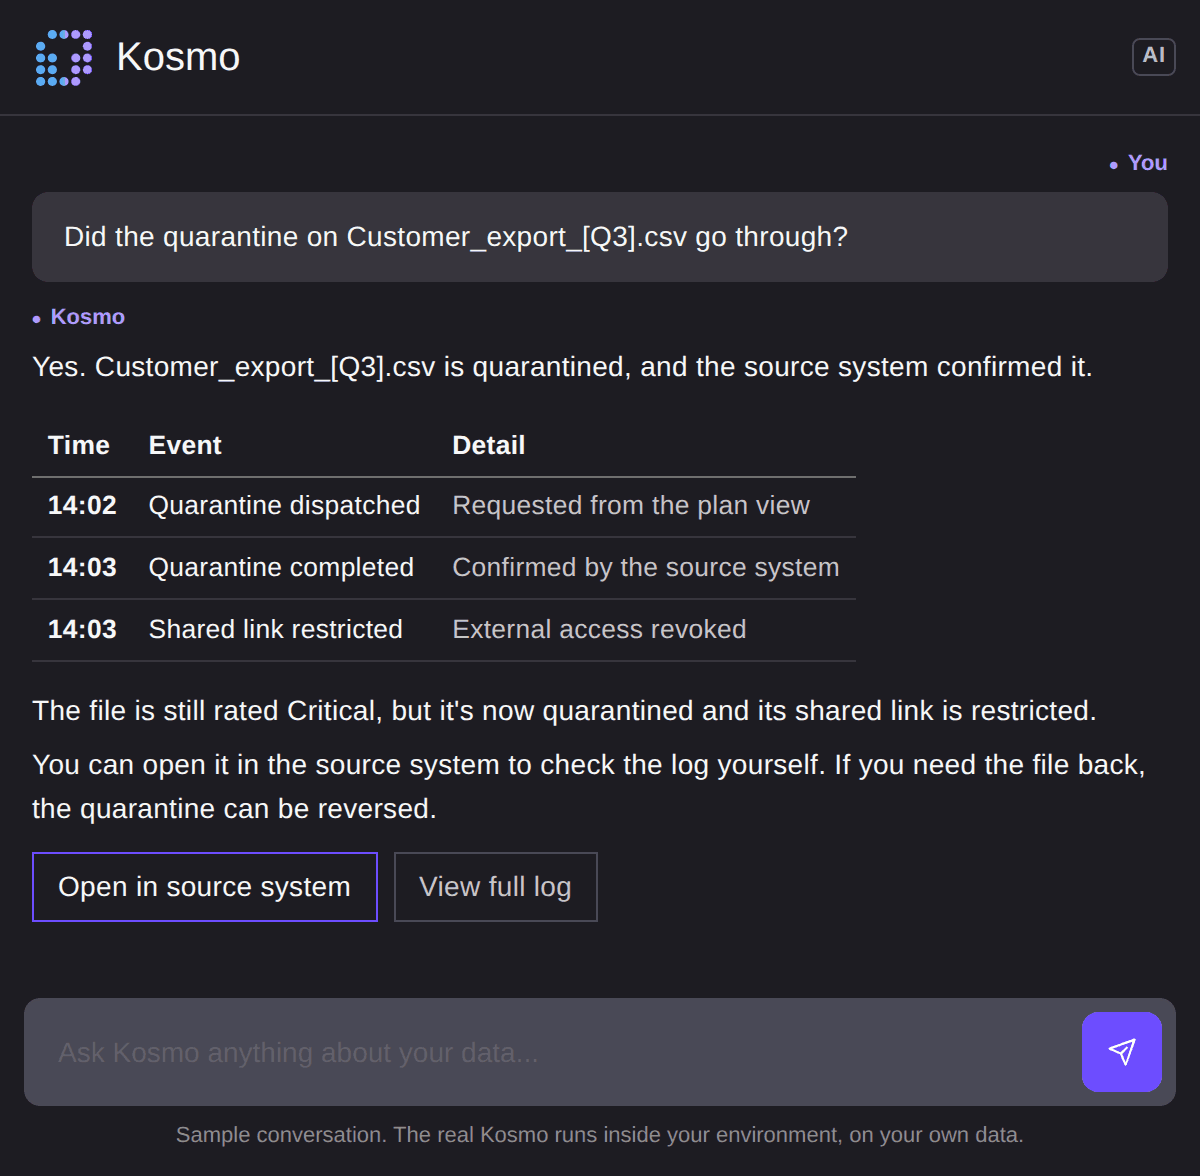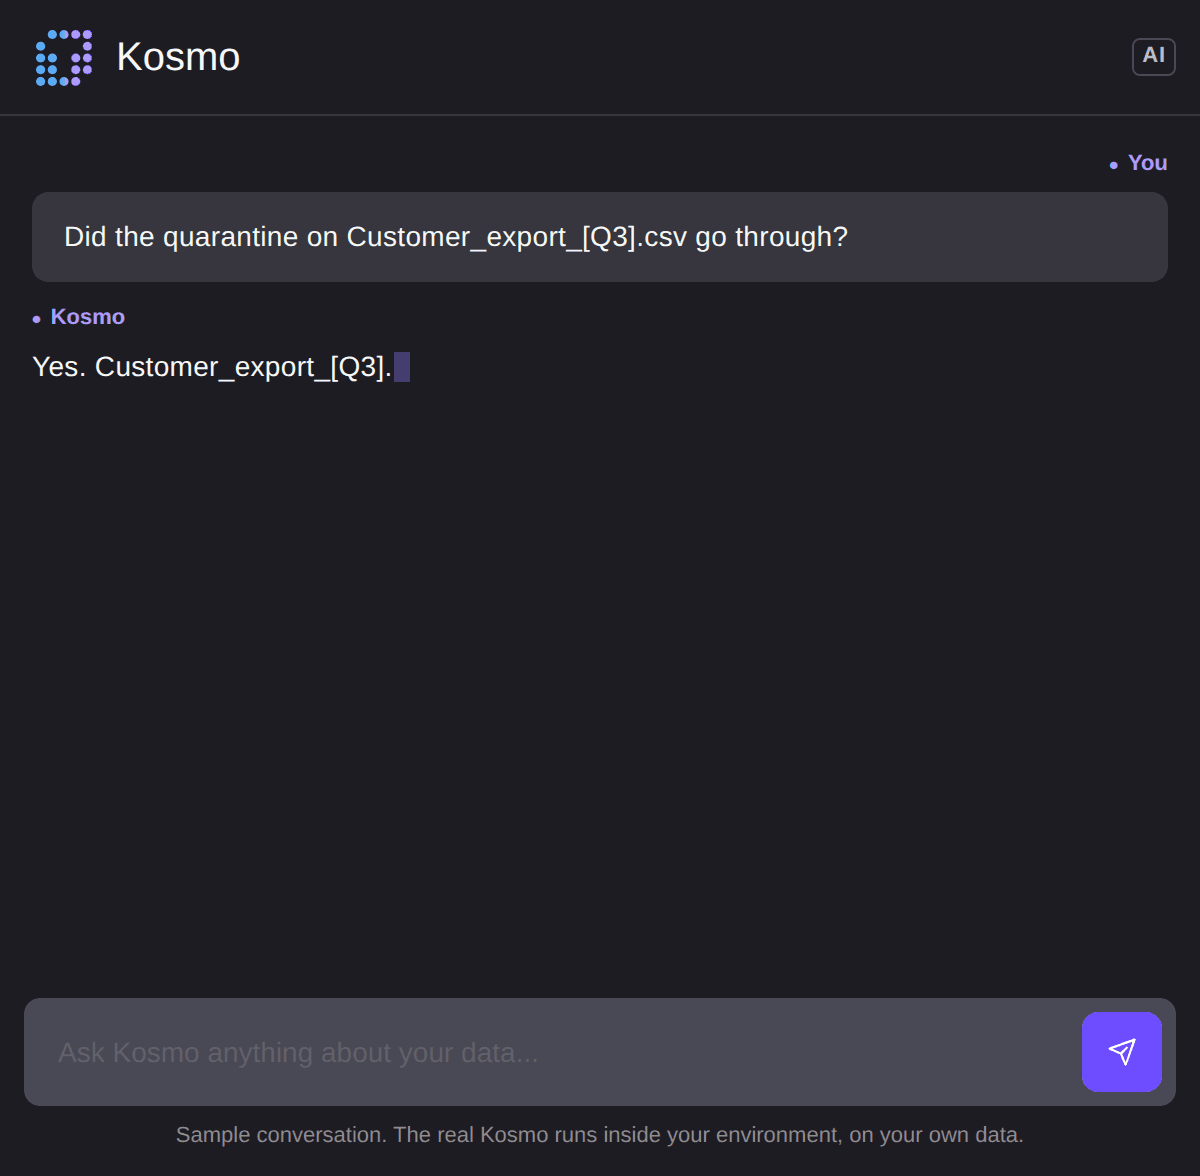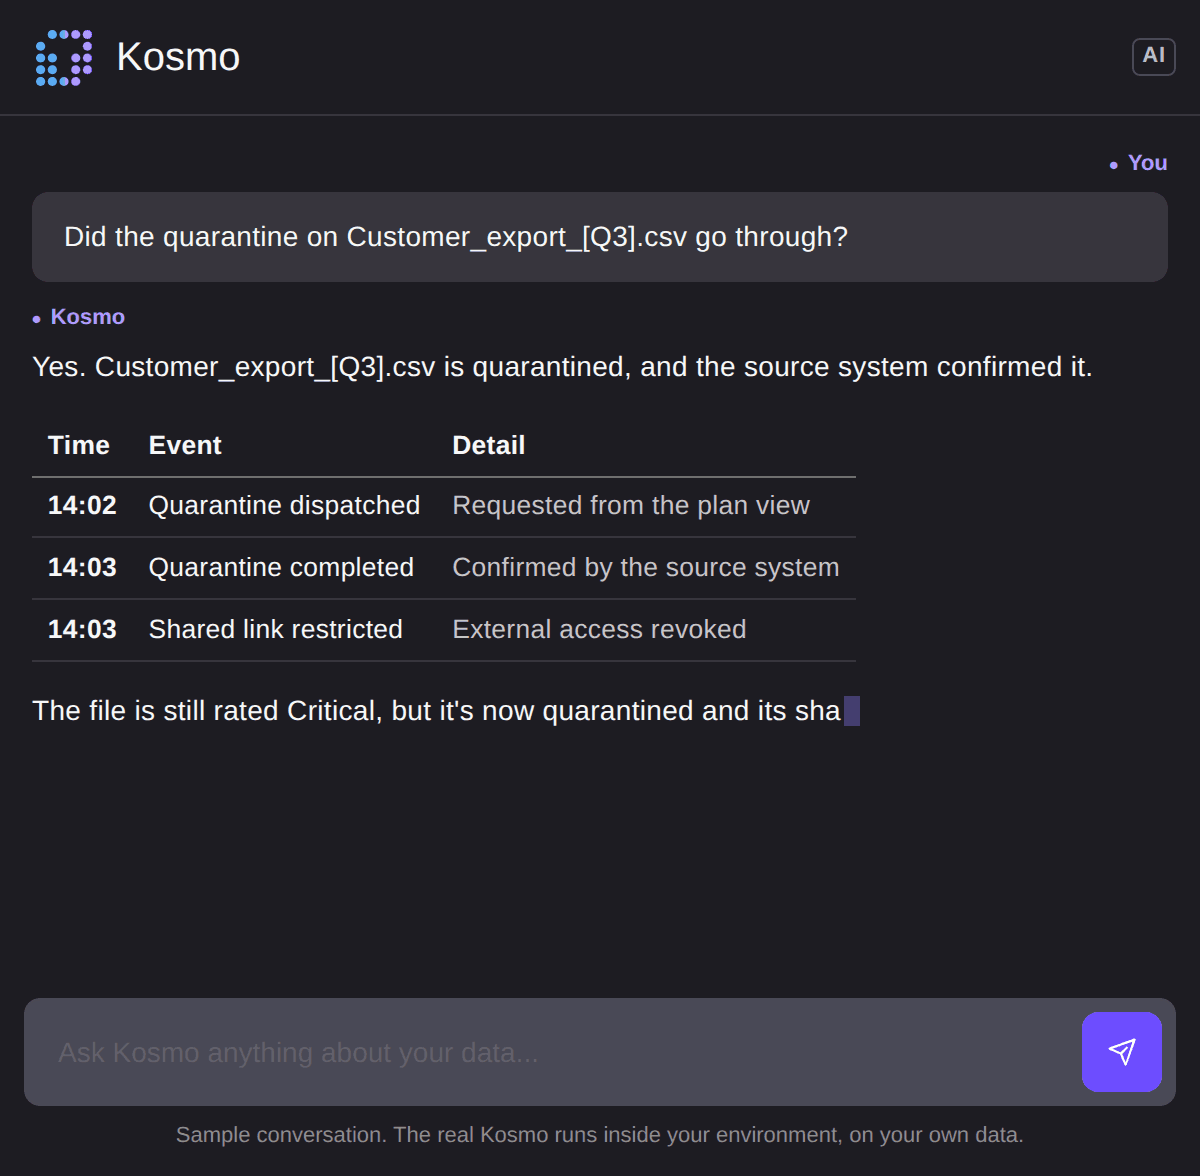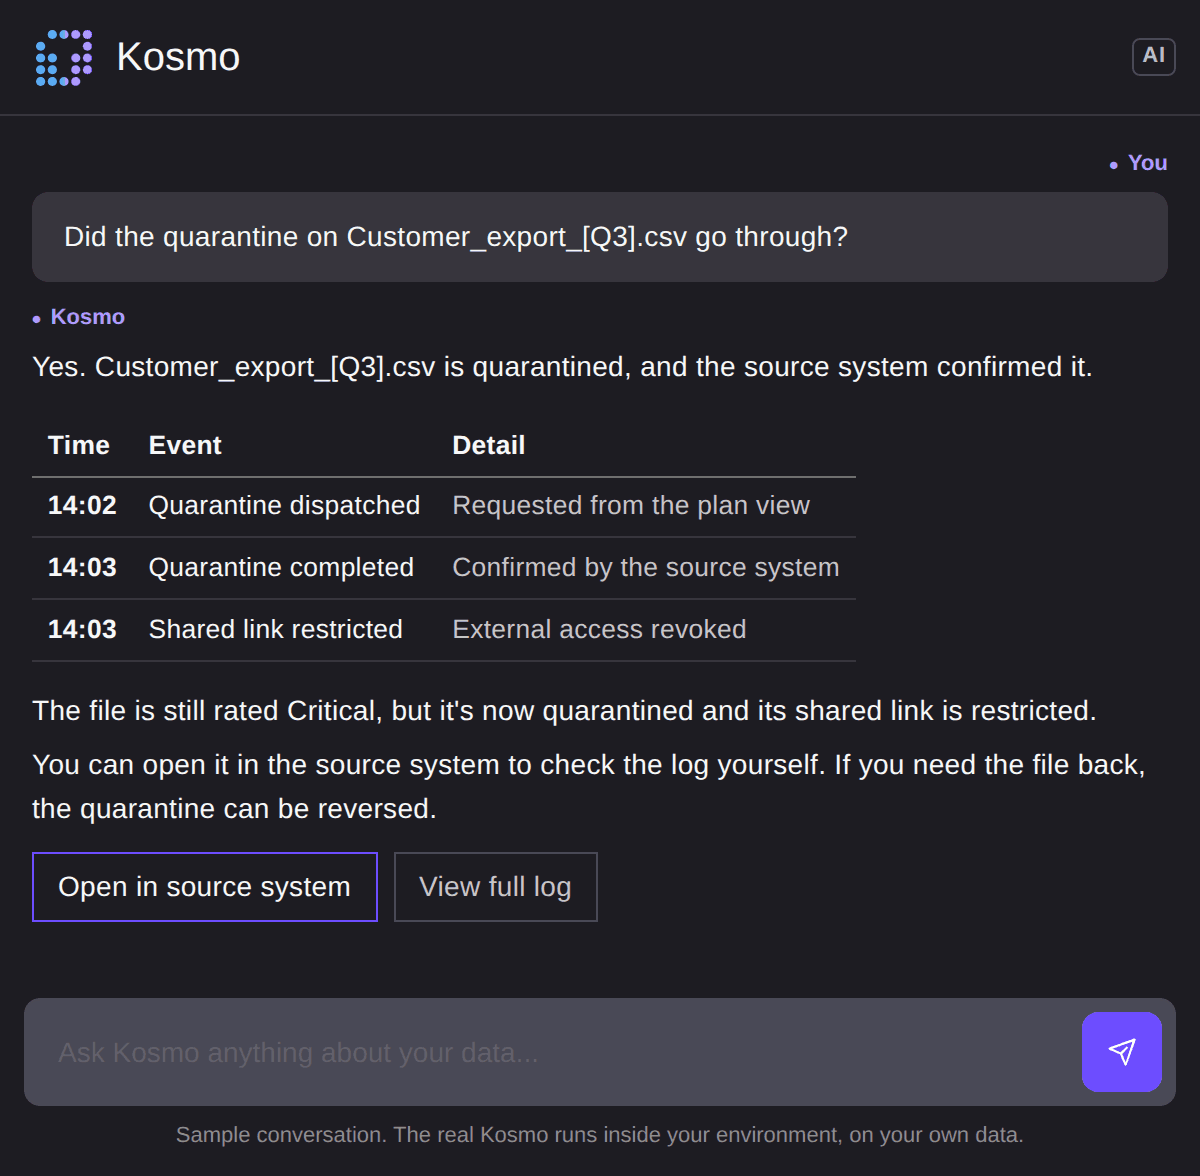
Review the plan, then apply the action inside the same interface. Open the resource afterward and the activity log shows the action dispatched and then completed, so you can confirm the file is quarantined rather than assume it.

Kosmo — Review, apply, verify
Kosmo

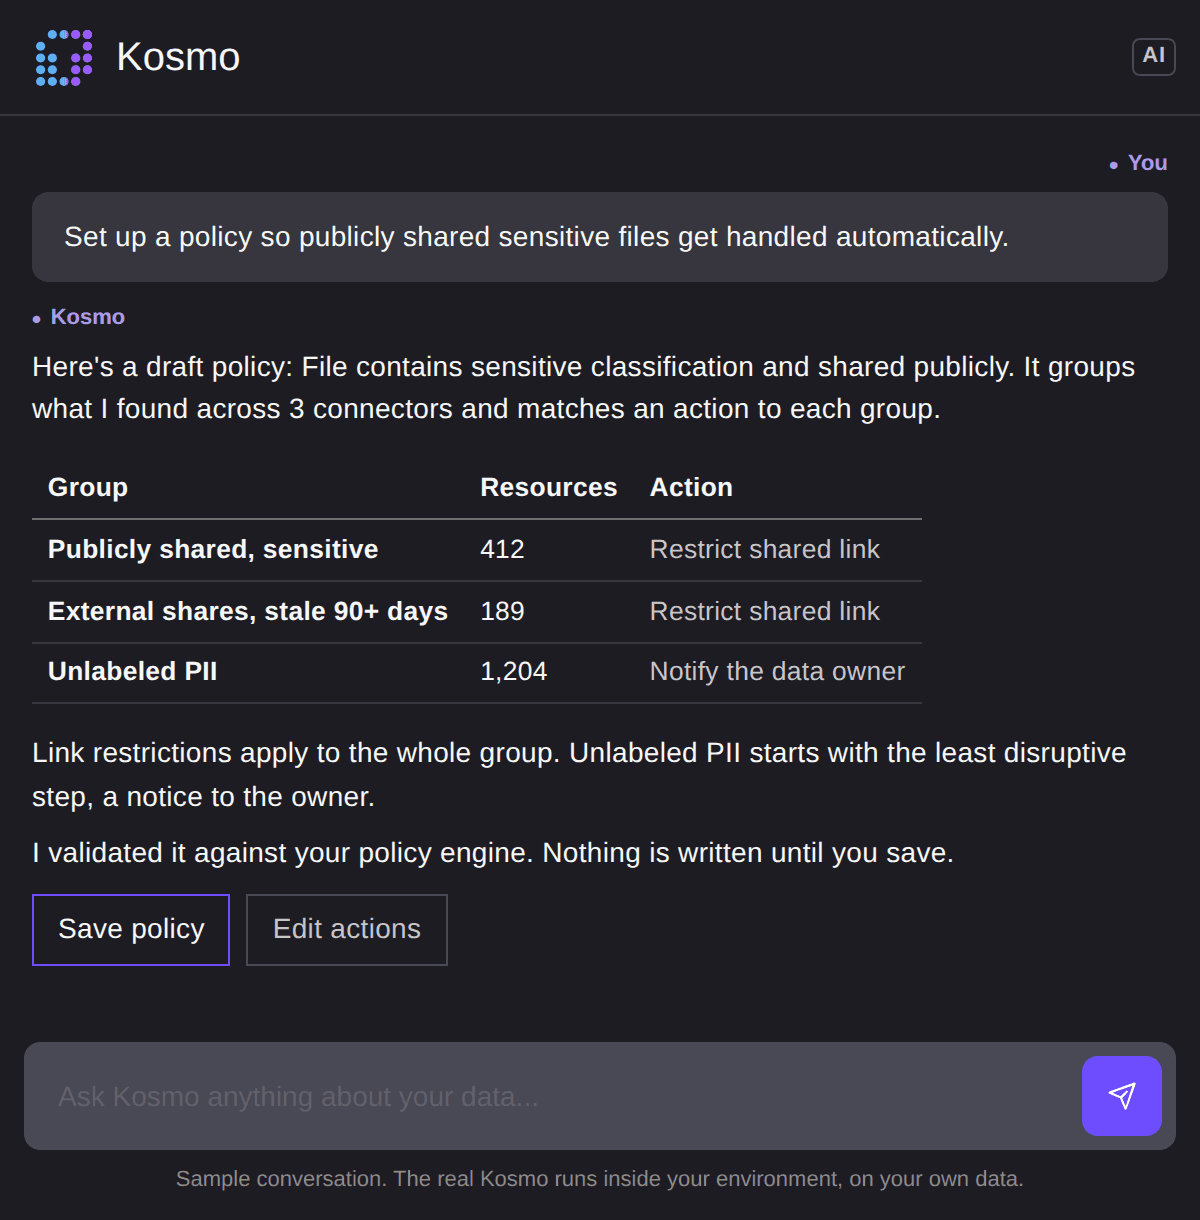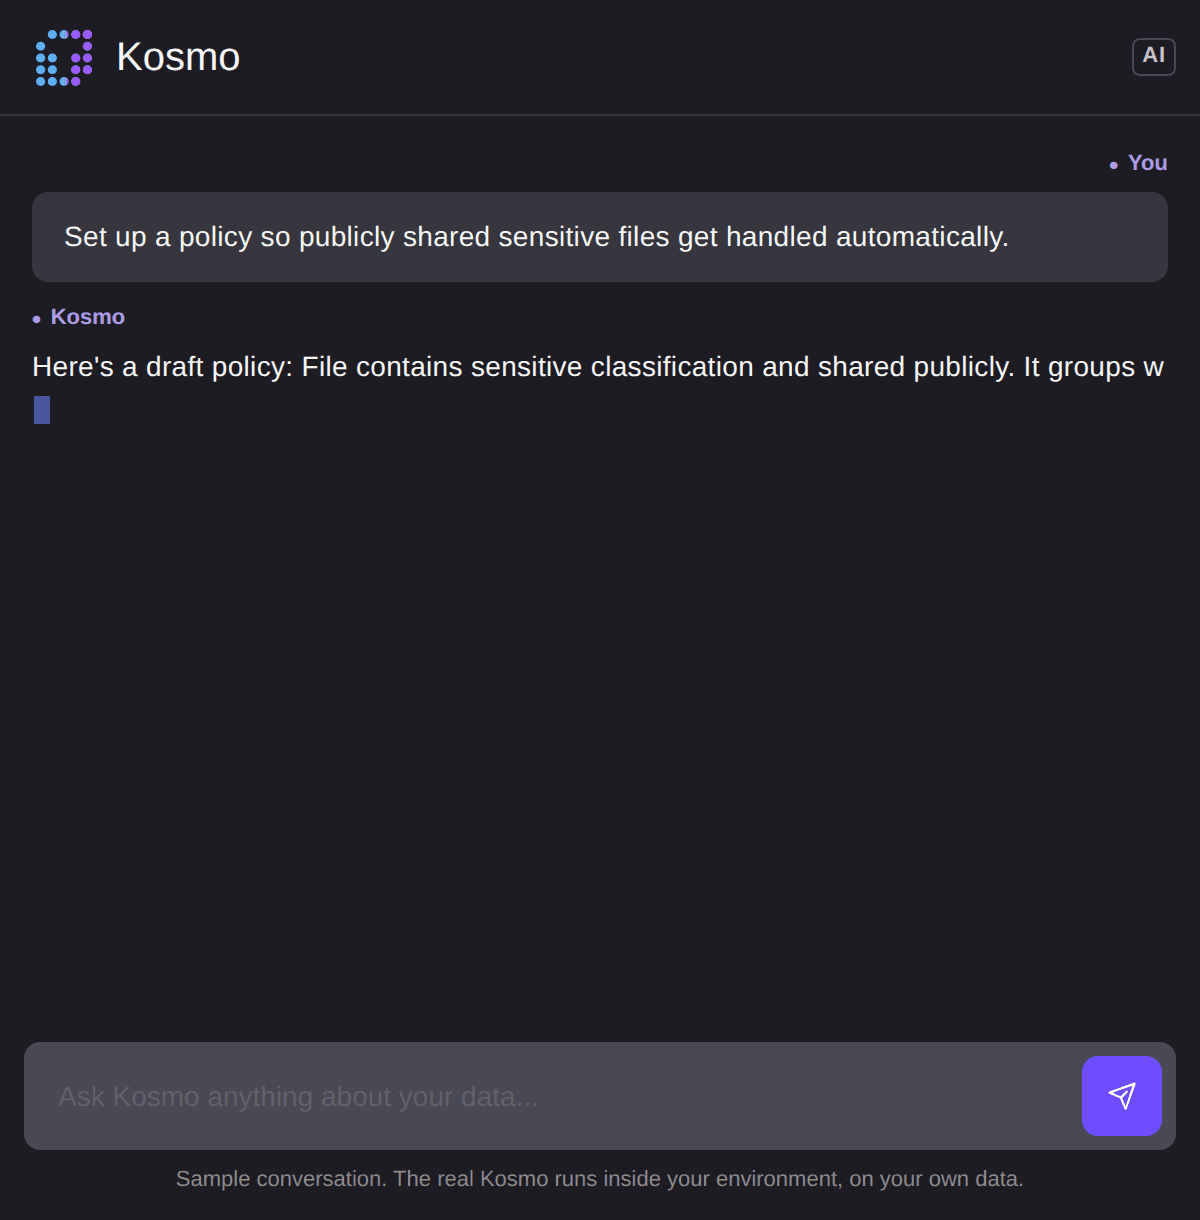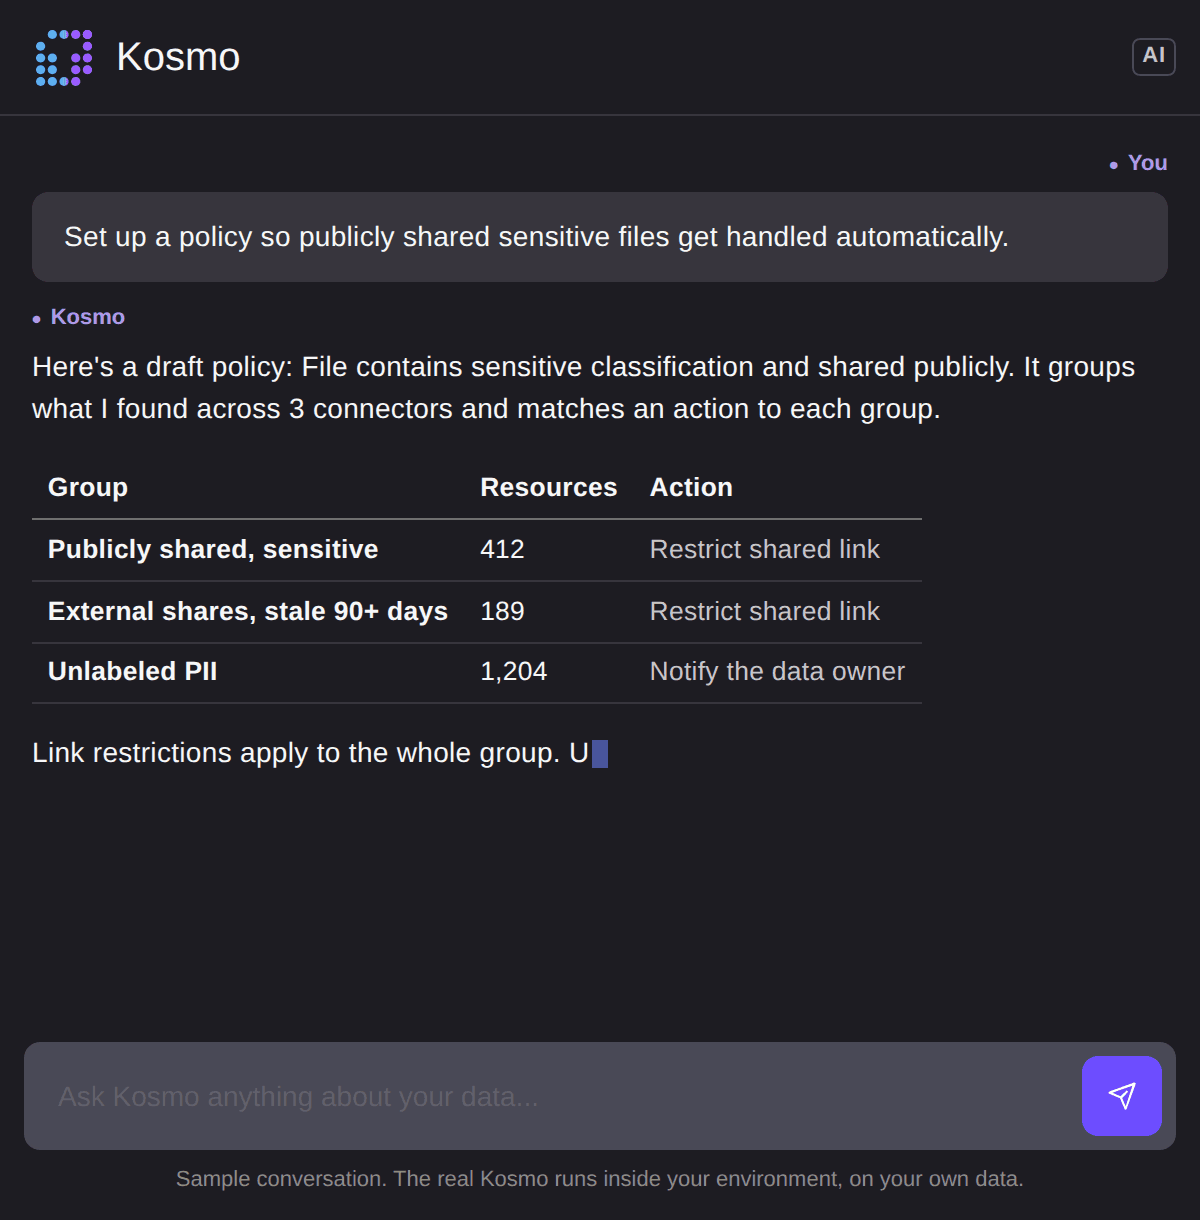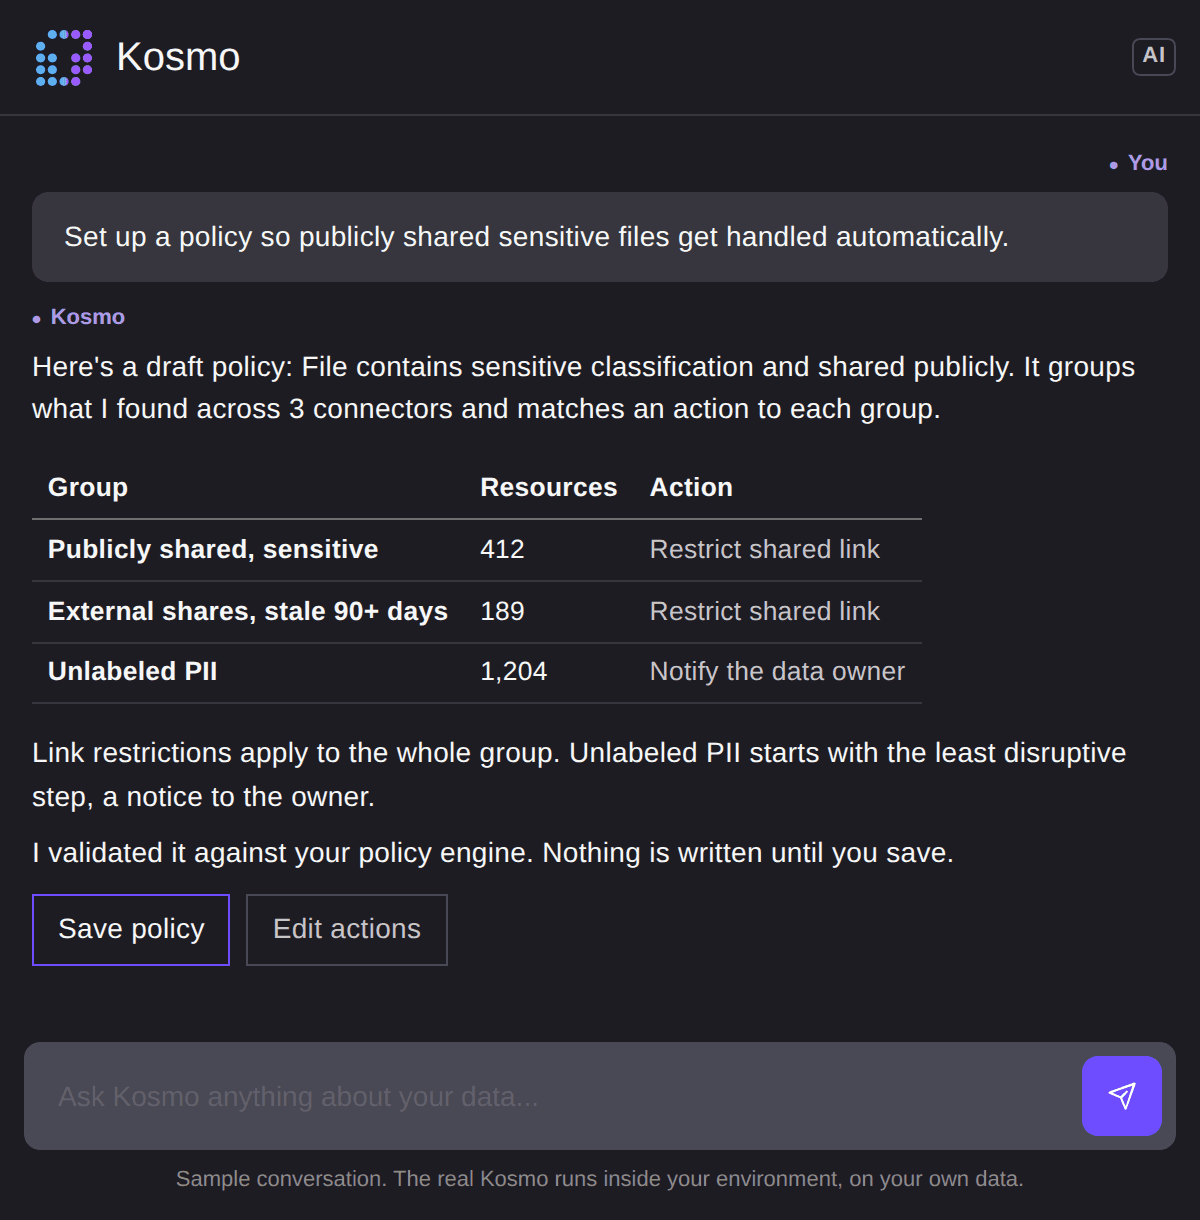
Alert triage at scale, then set policy

Ask Kosmo to triage and it groups related risks together, with real counts behind each group, so you can act on a pattern instead of a file.

‍

From those groups you can create a policy directly. Set the conditions Kosmo should watch for and name the action it should take. Kosmo validates the policy against your real policy engine and writes nothing until you save it. Once saved, matching resources get exactly the action you defined, no ticket required.

Kosmo — Alert triage at scale, then set policy
Kosmo

Report to any audience

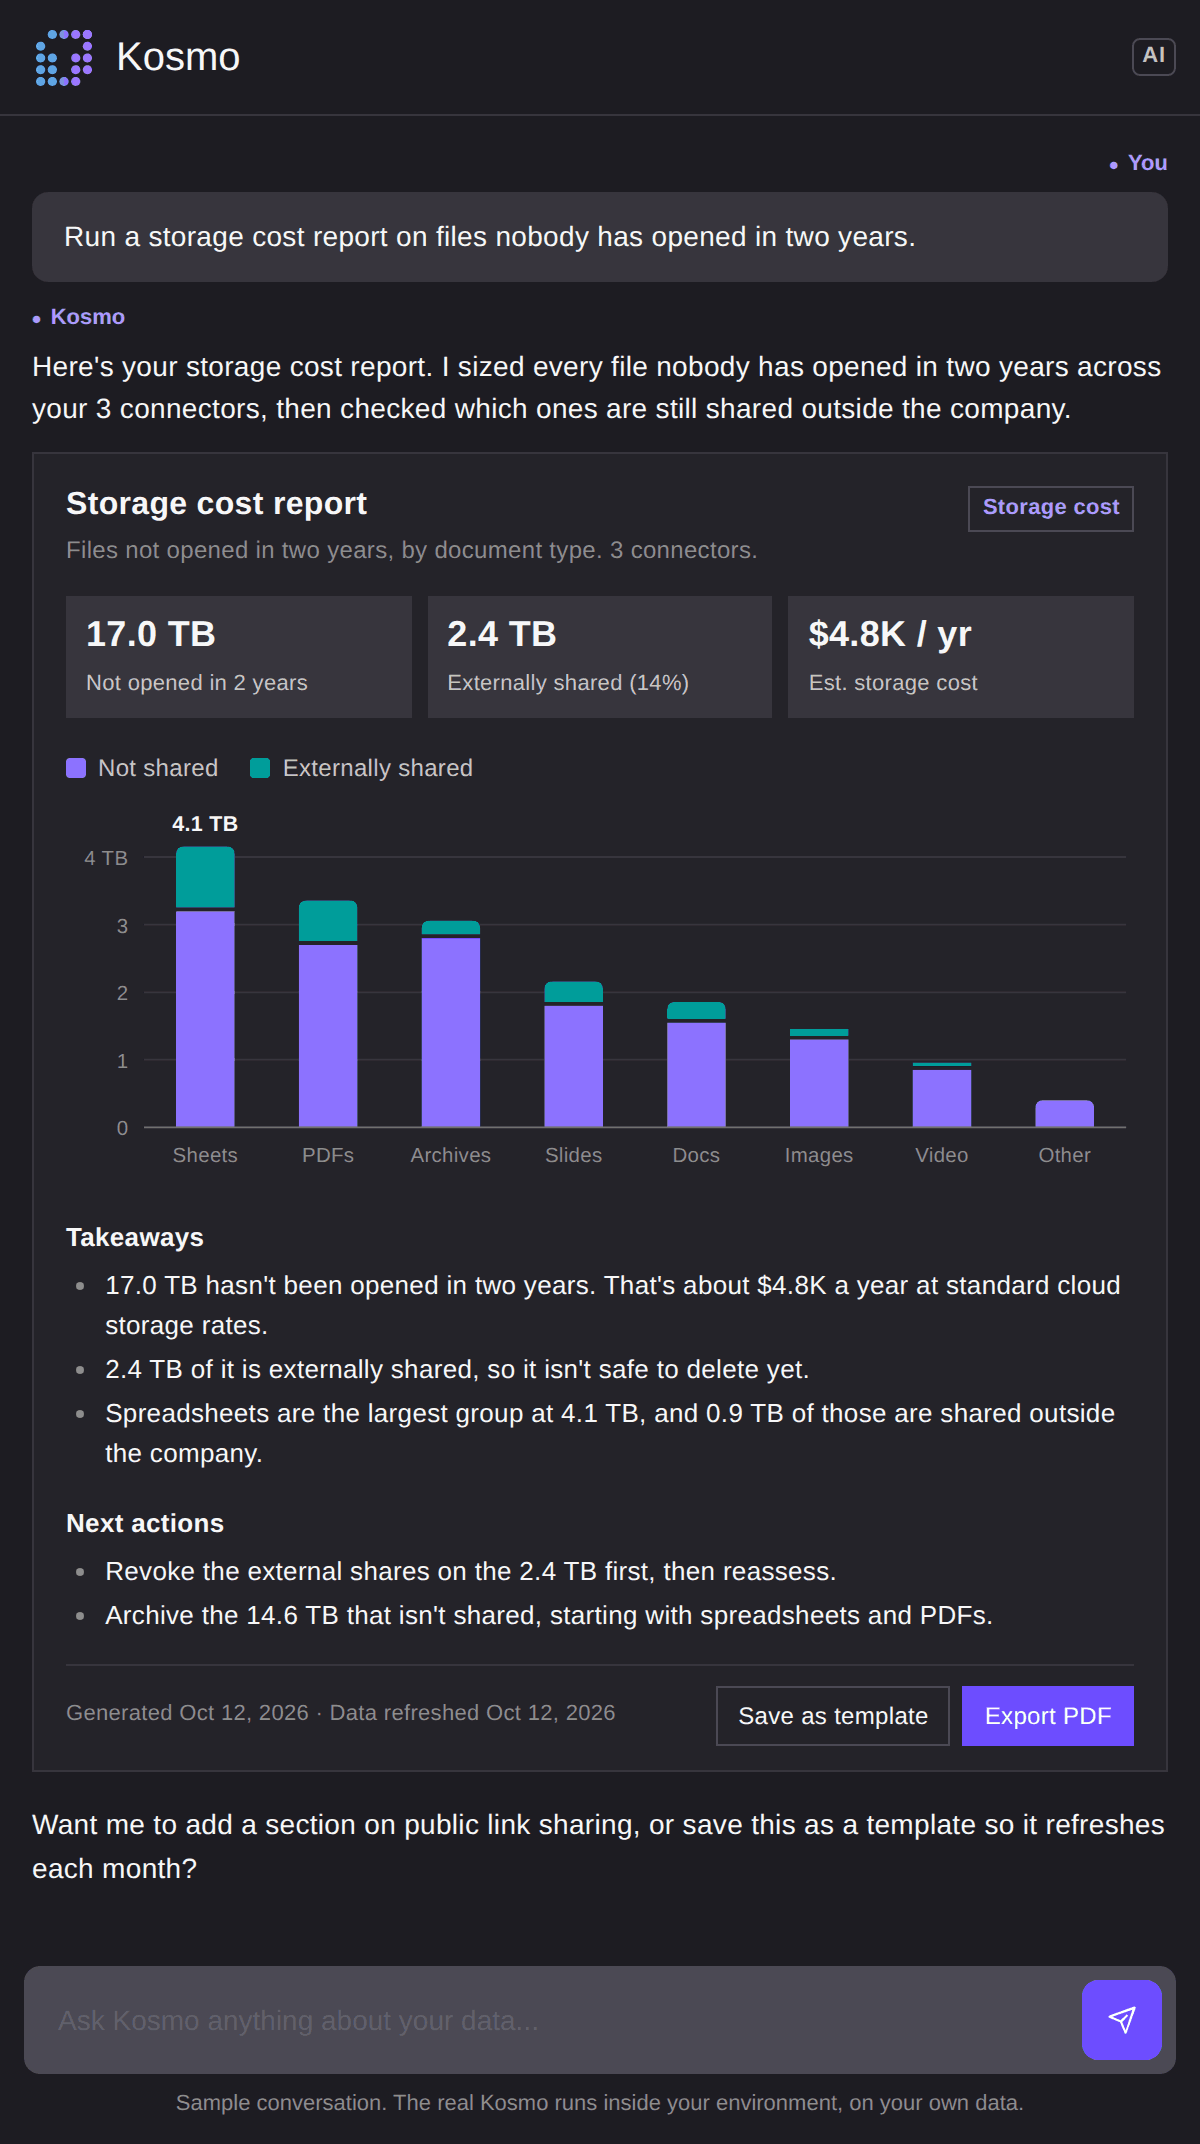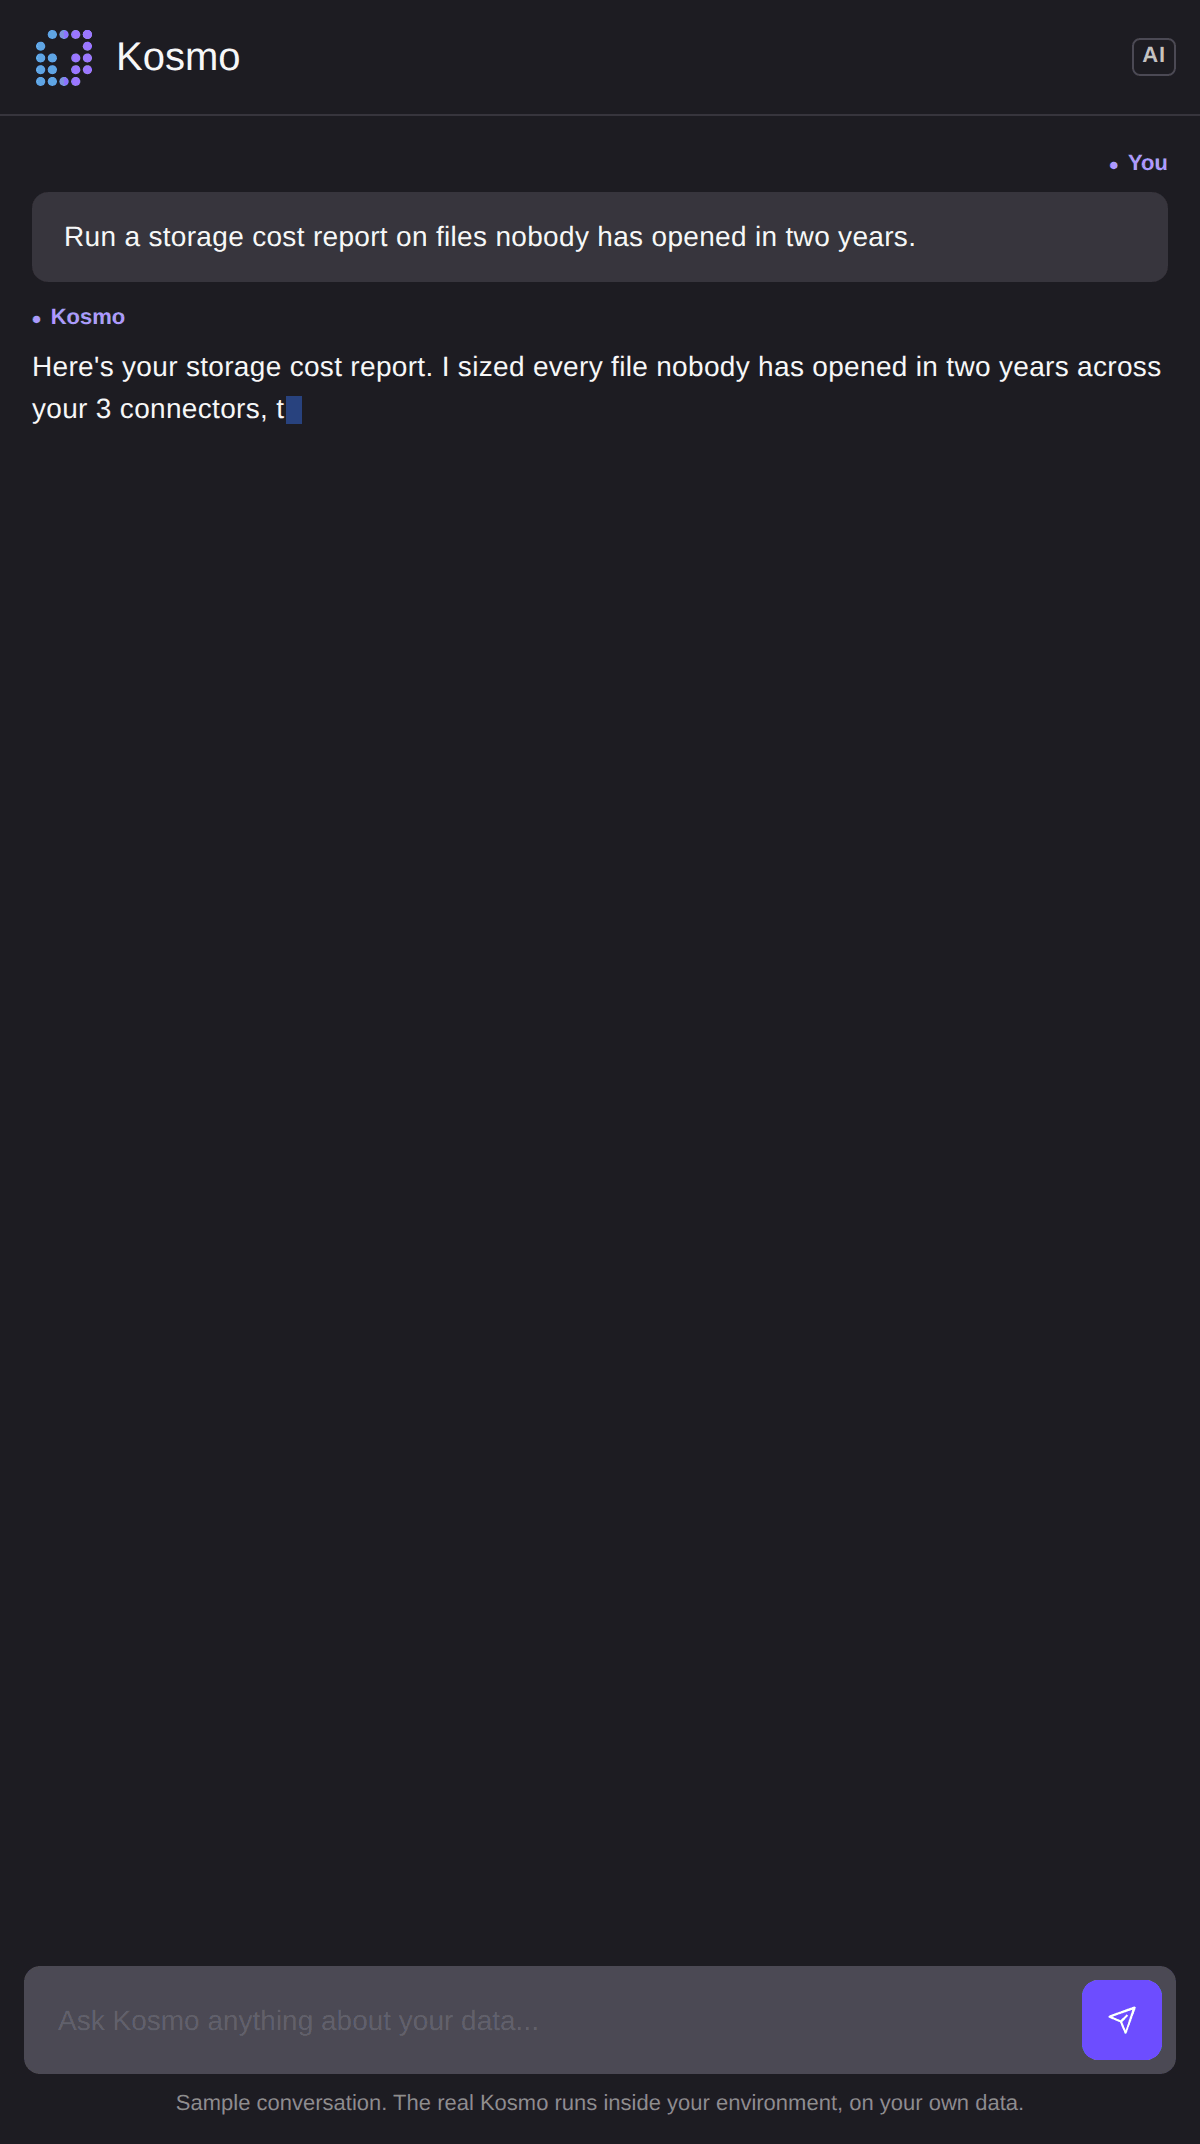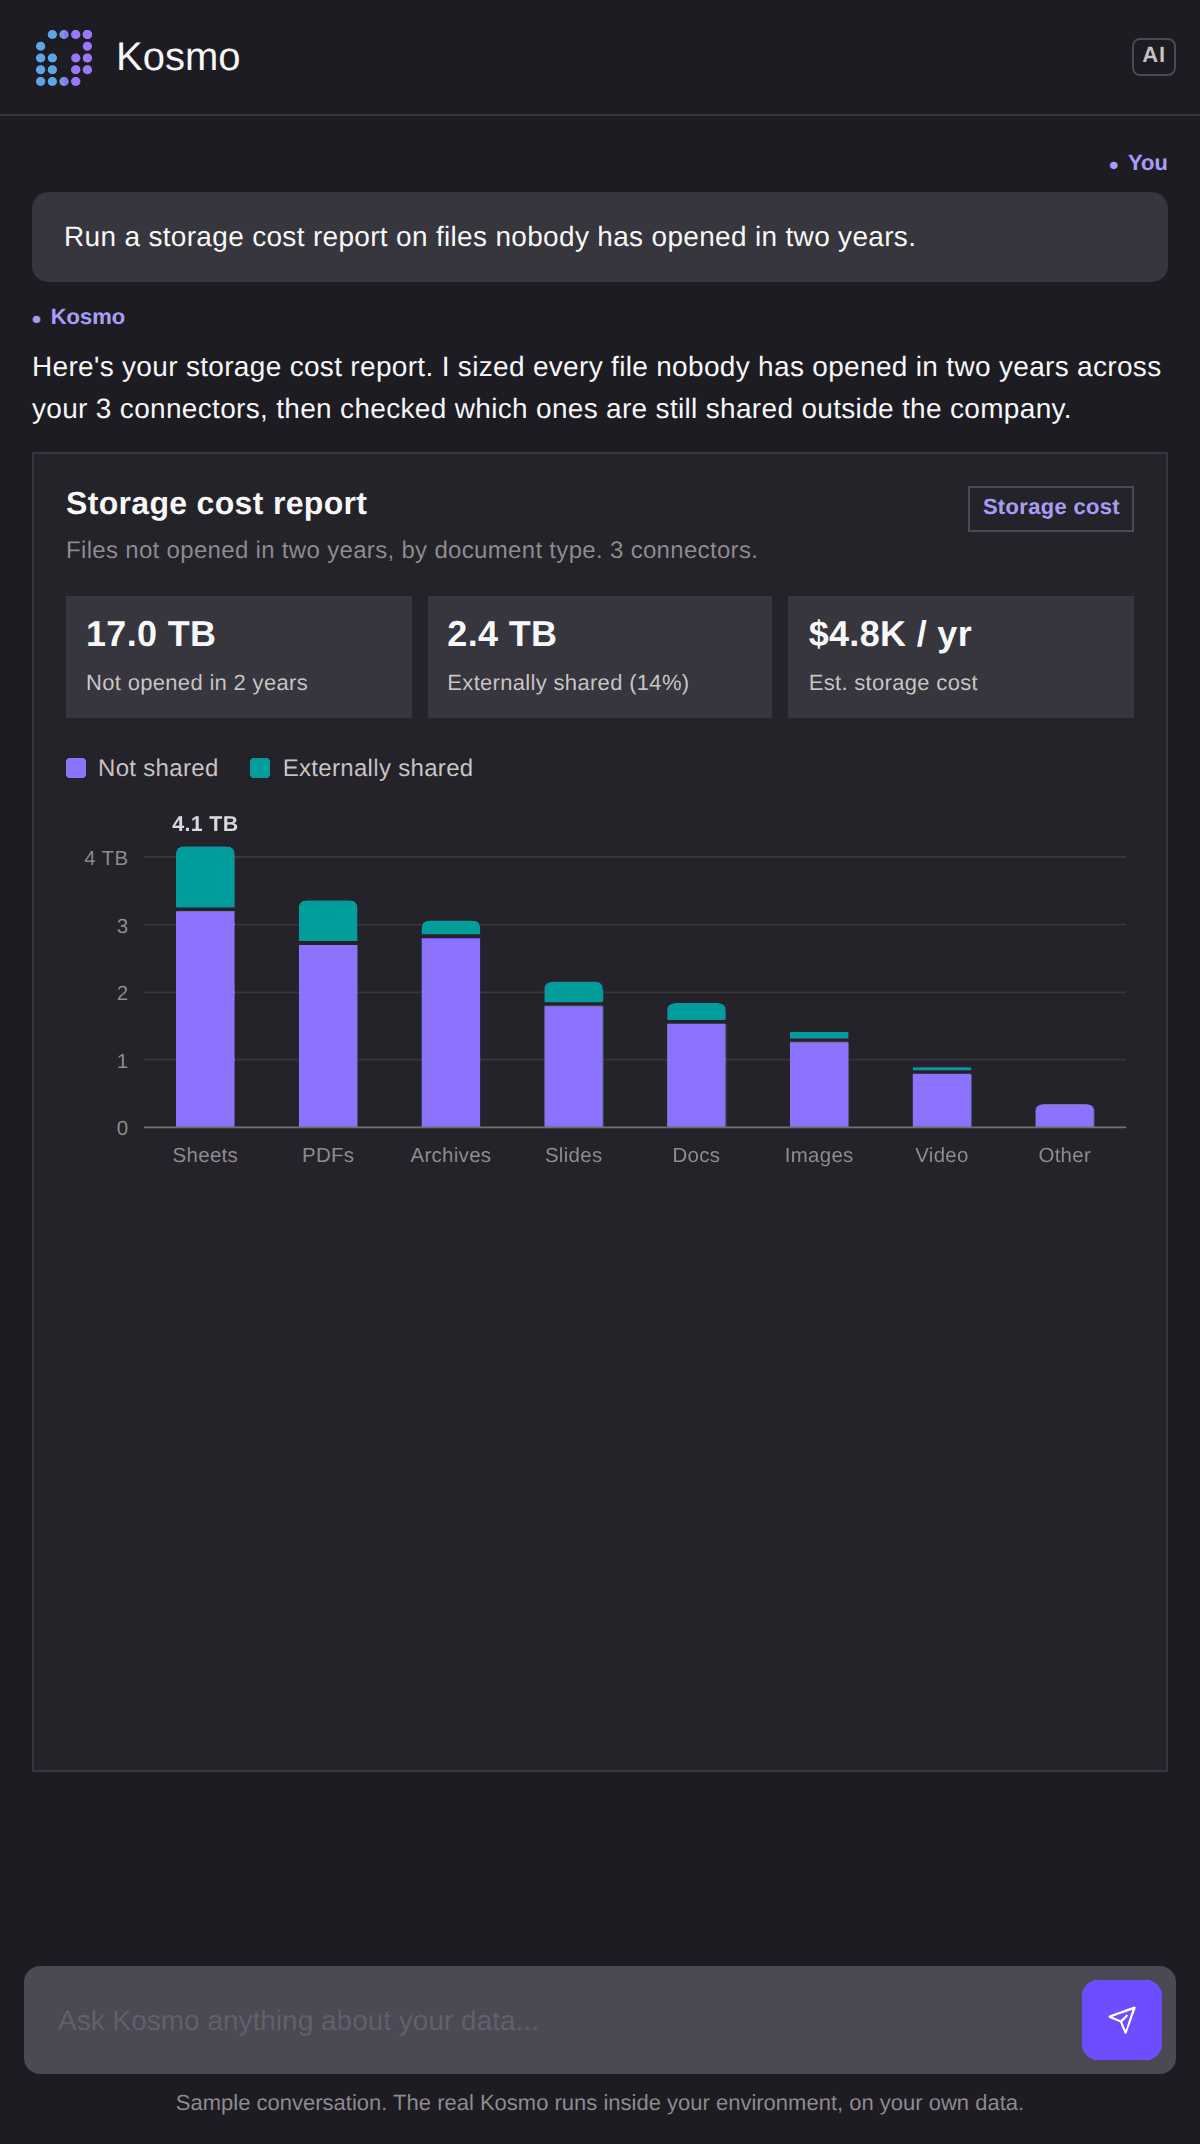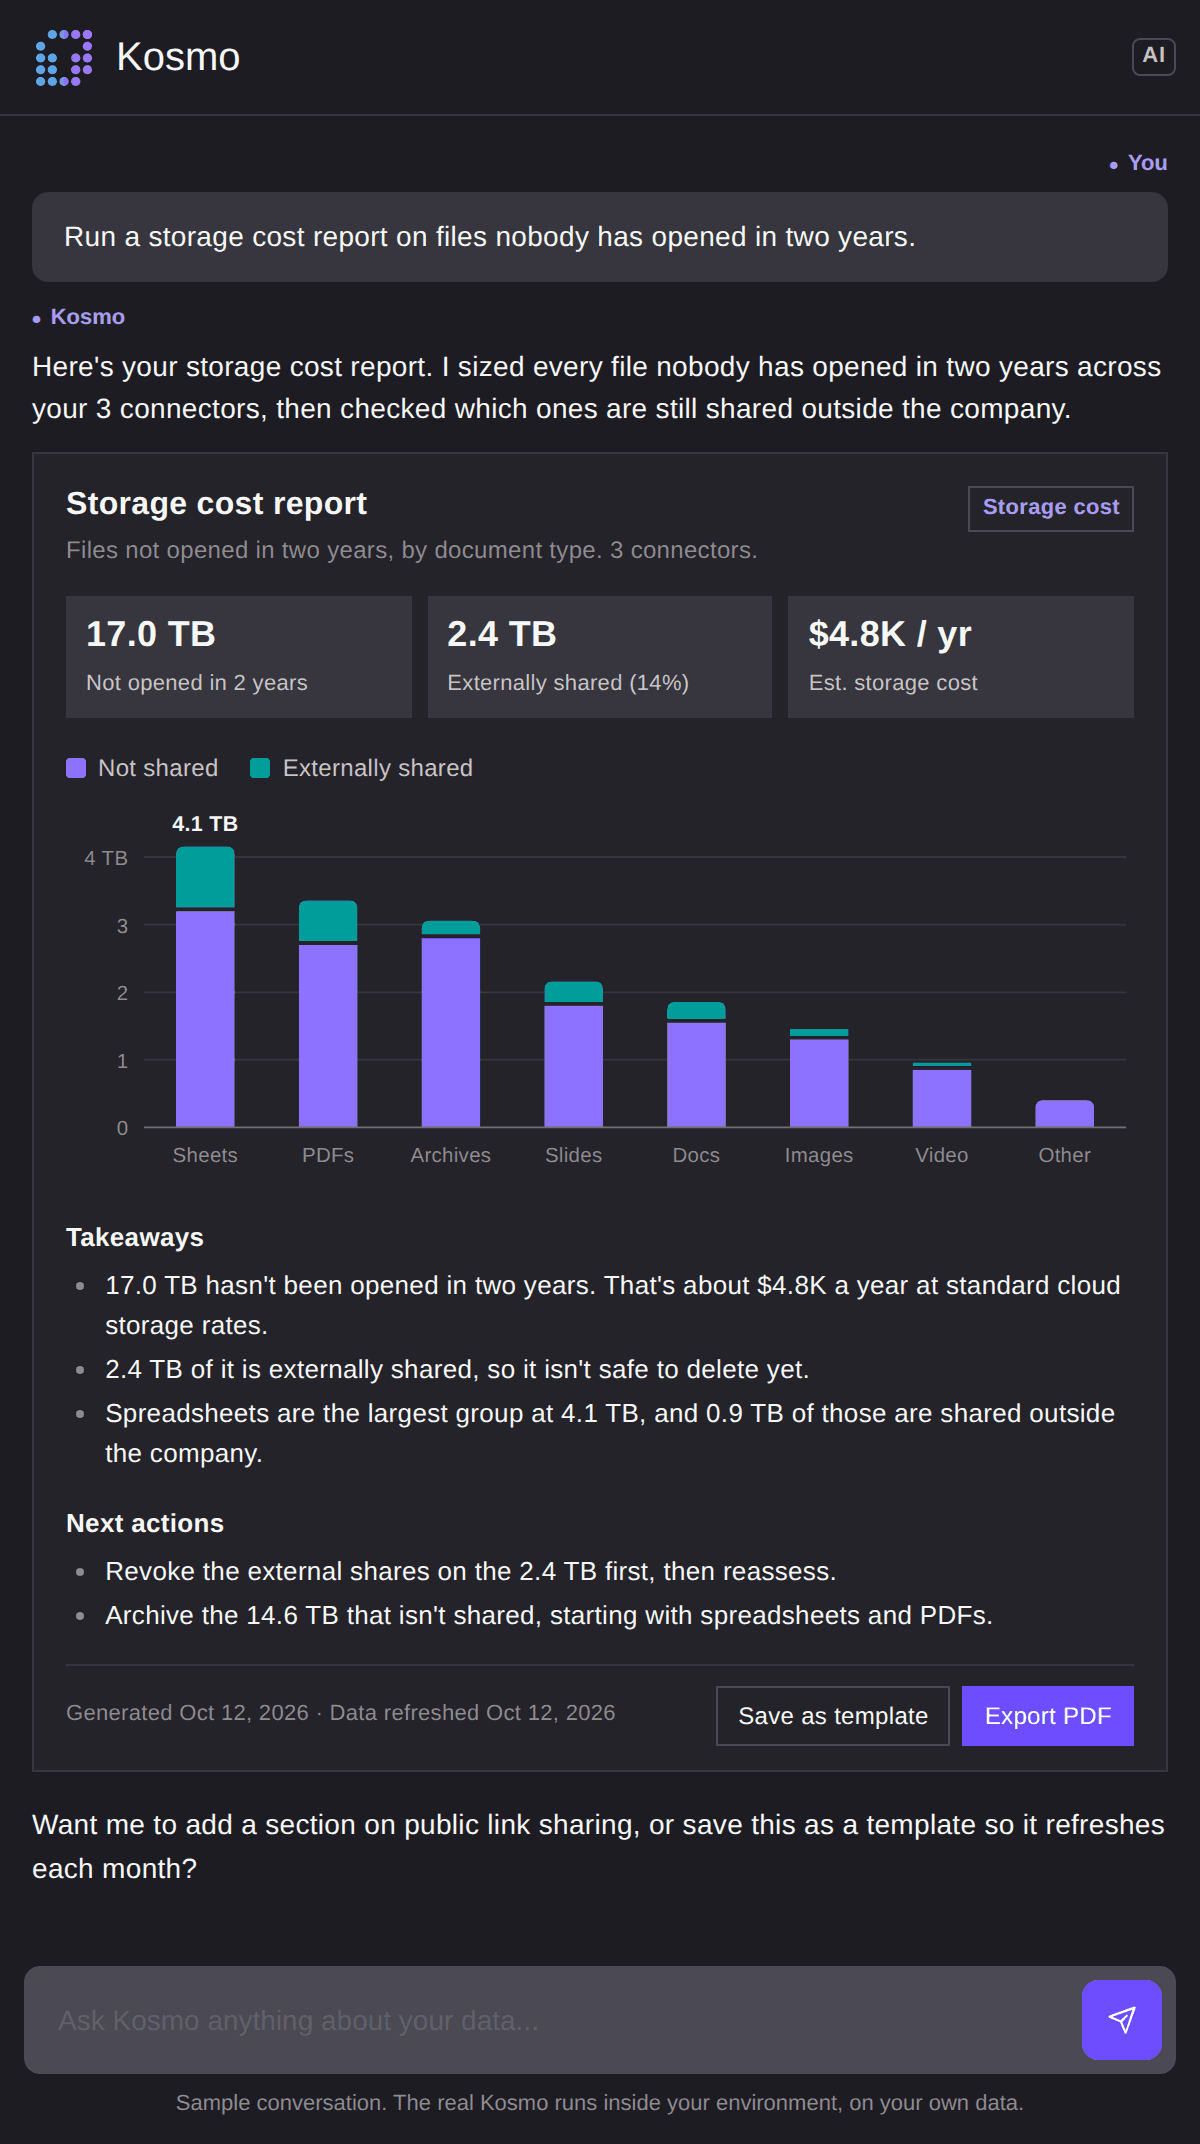
Ask Kosmo what it can report on and it lists its nine built-in report types, from exposure and access risk to public sharing to storage cost. Pick one and it runs the numbers against your data, then writes takeaways and next actions under each chart. Ask for a storage cost report, for example, and it sizes the files nobody has opened in two years, flags the ones that are externally shared as not safe to delete, and suggests revoking the share instead.

‍

Edit it the same way you asked for it. Add a section on public link sharing, drop in your logo, switch to your brand colors or dark mode, and export to PDF.

‍

Save it and it becomes a template. Refresh reruns the queries against current data, so last month's report becomes this month's without rebuilding it, and every version records when it was generated and when the data was last refreshed.

Kosmo — Report to any audience

Reports your whole org can read. No BI tool required.

Most security reporting is built for the people who run the tool. Kosmo builds it for the people who read it.

Built for the audience you name

Built for the audience you name. Ask for a report for legal, privacy, HR, or leadership, and Kosmo shapes it for them. Every chart comes with written takeaways and next actions, so the report explains itself.

No builder, no fields to pick

Describe the report you want in plain language. To get you started, nine built-in report types cover exposure, access risk, public sharing, and storage cost. Then you can edit any section the same way you asked for it or build from scratch if desired.

Numbers you can rerun

Kosmo doesn't write its own queries. A validated form compiles them the same way every time, so the same question returns the same answer instead of starting another round of trial and error.

Last month's report, rerun

Save any report as a template and refresh it against current data. Each version records when it was generated and when the data was last refreshed, so you can show how your program is moving over time.

An agent that closes data risk, not one that just shows it.

Data security's future is not an allow-or-deny switch. It is a human and an agent working together, and knowing exactly when to hand off is what makes that trust possible.

Kosmo runs on the Data Reasoning Layer. Understand what the data is. Decide what should happen to it. Enforce that decision, once you approve it.

The answer is the entry point to the fix, not a dead end. Ask a question and the same surface carries a direct path to action, with no ticket and no separate tool. The moment you decide something is worth acting on is the moment you can act on it.

Detection, triage, reporting, remediation, and policy creation happen in one flow, and nothing changes in your environment until a person signs off.

Five steps, one agent.

How Aprio Operationalized Data Security with Teleskope
industry:

How Aprio Operationalized Data Security with Teleskope

How The Atlantic Reduced Time Spent on Data Deletions by 95% with Teleskope

How Ramp Achieves Real-Time Data Redaction with Teleskope

Ramp

"A lot of DSPMs, they identify the risk but don't automate the action. It kind of just works without me having to necessarily micromanage it at all times — which is a huge benefit for us because we just don't have that operational capacity."

Alvin Zhang
Security Ops
Aprio

"For the first time, we have a platform that not only finds sensitive data across our systems but also understands context and takes action automatically."

Lock Langdon
CISO
The Atlantic

"Teleskope was the only solution that did everything we needed, from data deletions to vendor coordination and PII detection. The platform has become a staple across our data security workflows."

Aline Rollenhagen
Executive Director of Data

Frequently Asked
Questions

Have more questions?
Contact us
Contact us
Got questions? We’ve got answers.

Could someone use Kosmo to see data they are not allowed to access?

arrow down

No. Every query runs under the permissions of the person asking, resolved outside the agent. If you can't open a file in your systems today, Kosmo won't show it to you either.

Does my data go to a model provider?

arrow down

Only metadata. Kosmo reasons over classification labels, counts, and resource identifiers. File contents never reach the model and stay where they are.

Is Kosmo a DSPM tool?

arrow down

Kosmo is the natural-language interface to Teleskope, which competes in the DSPM and DLP categories. The difference is where it stops. Most DSPM tools end at a prioritized finding. Kosmo takes the same finding through to a specific, reversible action you approve.

How do I know the numbers in a report or triage are real?

arrow down

Kosmo does not write its own queries. A validated form compiles them the same way every time, so the same question returns the same result, and you can rerun it to check.

Can people outside security use the reports?

arrow down

Yes. Kosmo builds reports for the audience you name, whether that's legal, privacy, HR, or leadership, and you can edit any section in plain language before exporting to PDF.

Will Kosmo delete or change things in my production environment on its own?

arrow down

No. Kosmo proposes a plan and stops there. The remediation agent has no tool that executes anything, so nothing changes until you approve it.

Is this just a chatbot layered on a dashboard?

arrow down

No. Every session ends in a structured output, such as a remediation plan, a triage group, a report, or a policy, not a paragraph of prose.

How long before my team gets value from this?

arrow down

Kosmo can start working as soon as Teleskope completes its first scan of your data. There is no new interface to learn. You ask in plain language on day one, and it gets sharper once you complete the onboarding questionnaire.

What is Kosmo?

arrow down

Kosmo is Teleskope's data security agent. You ask about your sensitive data in plain language and Kosmo returns a structured answer, then carries that answer through to triage, a remediation plan, a report, or a policy. It proposes actions rather than taking them, so nothing changes until a person approves it.

Do I need a BI tool to build custom reports?

arrow down

No. You describe the report in plain language, edit it the same way, and export to PDF with your branding.

Can I track progress over time?

arrow down

Yes. Save a report as a template and refresh it against current data. Every version is timestamped, so each month's report can be set next to the last one.

Related Products

Your backlog isn’t a resource problem. It’s a tooling problem.

See how Teleskope resolves high-confidence data exposure automatically 
— starting in your first session.
Book a Demo
Book a Demo